AI-POWERED COMPLIANCE AND AUDIT OS
Compliance that is done.Audit that proves.
Netra turns the work your teams already do into evidence, control status and an audit record that stands up to scrutiny, across every framework that applies to you.
Built for regulated organisations that run compliance in-house.
How the work connects
One task, completed once, counted everywhere it applies.
Finish the task once. The evidence behind it reaches the Compliance Centre, and the Audit Centre opens on it.
How the work connects
50+ frameworks in the library: India, the United States, Europe and the UK, and global standards
Explore the libraryGovernance, not paperwork
Due diligence. Due care. Both on the record.
A regulator or a board does not ask whether you meant to be secure. The question is narrower than that. Did you establish what you are responsible for, did you act on it, and can you show the two. Netra is built around those three questions, in that order.
- 1Due diligence
Establish what you are responsible for
Select the frameworks that apply to your class of entity and your markets. Policies follow from them. Risks go on a register, assets come into scope, vendors are profiled. The obligation is written down before anyone is asked to work on it.
Where it lives in Netra
- 2Due care
Do the work, and keep the proof of it
Every policy statement becomes a task with a named owner, a due date and a recurrence where the control is periodic. Evidence is attached to the work itself, not collected later. Control status is derived from what is finished, so nothing is marked compliant because somebody typed it.
Where it lives in Netra
- 3Proof
Show it, to anyone who asks
The audit opens on evidence that is already in place, with the auditee, the managing consultant and the external auditor working in the same record. Board papers come off the same data. Nothing has to be reassembled for the occasion.
Where it lives in Netra
Compliance that is done. Audit that proves.
Done this way, the work itself is the record. Due diligence is visible in what was established, due care in what was completed, and both stand up without a fire drill before the audit.
See how it runsConnected, not collected
One operating system. Every module on the same record.
Work happens once, in the Task Engine. Every other module reads from that work, so nothing is re-keyed and nothing drifts out of date.
Task Engine
Where the work is done
Framework requirements arrive as tasks with owners and due dates. Each task shows every framework it satisfies, and recurring tasks keep evidence current.
One completed task updates
Compliance Centre
Status derived, never typed
Live control status for each framework, worked out from completed tasks and evidence.
Policy Hub
Policies that move with the work
A policy library generated at onboarding, with a score that rises as the work behind each policy is done.
Risk Manager
Risk treated by real work
A risk register with inherent and residual heatmaps. Risks come down as the linked tasks are completed.
Audit Centre
Audits that start with evidence
Internal, external, certification and regulatory audits end to end, with evidence already in a tamper-evident vault.
Third-Party Risk
Vendors you actually pay
Find vendors from what Accounts and Purchase pay, assess them through a vendor portal and record each decision.
Asset Management
Know what each task touches
An asset register linked to tasks, so you know where to act and which evidence applies.
Dashboard & Reports
One click to the board
A live Posture Score, a one-click board report for each framework, audit reports and third-party risk reports.
Netra AI
A co-pilot, not an autopilot
Works from your organisation's own records to show what evidence is missing and draft SOPs. It never changes status on its own.
Outcomes
What changes when the work is connected
Months to weeks
Audit preparation
Evidence from day-to-day work is already in the Audit Centre. The audit does not start from a blank page.
Once
Evidence collection
Upload evidence once against the task. It counts towards every framework that control serves.
Derived
Control status
Status comes from completed tasks and evidence, never typed in, so every number traces back to a file.
Tamper-evident
Evidence vault
Evidence is stored with a trail of who added it and when, so an auditor can rely on it.
After you sign
What the first weeks look like
No blank system to fill in. Your frameworks decide the policies, the policies decide the tasks, and the evidence starts building from the first week.
- Week 1
Scope and set up
- Choose the frameworks you are held to, by entity class where that applies
- Your policy library is generated from them
- People and roles added, with access set by role
- Week 2
Owners and assets
- Tasks arrive from the policies, each with an owner and a due date
- Assets and cloud accounts connected, so tasks know what they protect
- Vendors brought in from what Accounts and Purchase already pay
- Weeks 3 to 4
Evidence and the first view
- Evidence attached to the work as it is done, not gathered afterwards
- Control status appears on its own, derived from what is finished
- First posture view and a board pack you can table
How long this takes depends on your scope, how many entities you run and how quickly owners are named. Netra does not change your controls; it puts them in order.
Every stakeholder gets the answer they need.
CISO AND HEAD OF SECURITY
Where do we stand, and what moves it?
A posture score and framework progress that come from completed work.
COMPLIANCE AND INTERNAL AUDIT
Can we prove it, quickly?
Evidence, findings and actions in one trail, ready when the auditor asks.
BOARD AND LEADERSHIP
Is the risk under control?
Summaries drawn from live records, not assembled the night before.
START WITH YOUR OWN FRAMEWORKS
Tell us which frameworks apply to you and we will show them running in Netra.
Framework library
Any region. Any industry. One library.
India’s regulatory frameworks beside the global standards your customers and auditors ask for, across financial services, government, healthcare and technology. Over 50 in the library, each loaded control by control, each with a page of its own.
RBI CTRRAF 2026 Directions
Loaded control by control, with your entity class deciding the chapter set. Your first job is assigning owners, not interpreting the document.
Built for YourUnique Needs
Whether you are a growing company or a large enterprise, Netra adapts to your role, industry and scale.
Who Netra Is Built For
CISOs, compliance leads, internal audit, IT teams and the board, each with the view they need.
Industries We Serve
Our priority sectors, each with the frameworks Netra supports for it.
Solutions by Company Size
From growing companies to large enterprises, with the same platform and the same evidence.
By Region & Compliance
A library of 50+ frameworks, grouped by region, with a Framework Selector to find yours.
Made in India.
Made for the world.
Built in Bhopal by Army veterans and security practitioners, for organisations that answer to a regulator, a customer or an auditor, wherever they are. India’s own requirements are carried in full depth, and so are the standards the rest of the world asks for.
Built in India
Shlokcent Technologies Pvt. Ltd., registered in India under CIN U58202MP2023PTC064946 and headquartered in Bhopal. Founded and run by Indian Army veterans alongside security practitioners.
India in depth
The RBI CTRRAF 2026 Directions by regulated entity class, CERT-In, NISPG and MeitY CSA, loaded control by control rather than summarised.
See the Indian frameworksThe world beside it
ISO 27001, SOC 2, PCI DSS, GDPR, NIST, DORA, NIS 2 and HIPAA, across the United States, Europe and the UK, and global standards.
Browse the libraryDelivered anywhere
MSSPs, vCISO practices and audit firms run their own clients on the Partner Portal, each client in a workspace of its own.
The Partner Programme
Provable, not promised
Built to satisfy an auditor and a CISO
A compliance system has to be trustworthy itself. Every record in Netra can be traced to a person, a task and a file, and the controls around your data are part of the product, not an afterthought.
Read the security FAQsTamper-evident evidence
Show that evidence has not changed since it was submitted.
Append-only records
Consent records and the security audit log cannot be edited or deleted.
MFA on every account
Multi-factor authentication is part of account set-up.
Role-based access
Each person sees only what their role allows. Auditors see only what is in scope.
Isolated by organisation
Each organisation's data is kept separate, for Netra AI as well.
Your storage or ours
Netra's cloud by default, or your own cloud or drive, such as Azure Blob, Amazon S3, Google Drive, SharePoint, Dropbox Business or Box.
AI advises, people decide
Netra AI drafts and suggests. It never changes task status, evidence or compliance status on its own.
Privacy requests tracked
Erasure and export requests are tracked against a 30-day timeline, supporting GDPR and DPDPA.
Who builds Netra
Built by people who have been accountable for it.
Netra is built in India by Army veterans and security practitioners who have carried the responsibility themselves, in organisations where an audit finding mattered.
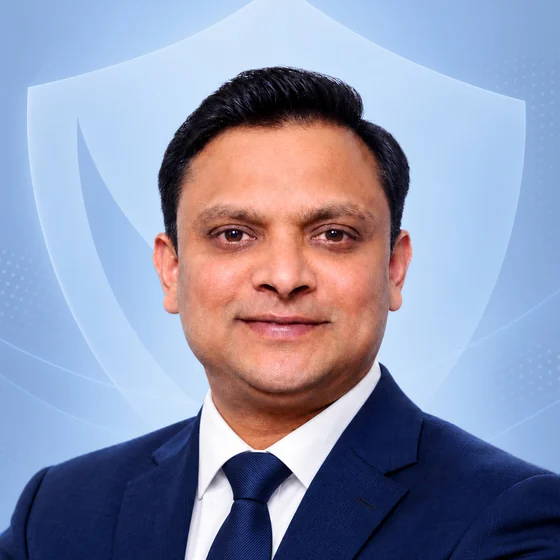
Col Saurabh Agrawal, SM (Retd)
Founder and Chief Executive Officer
Twenty-five years in Indian Army ICT and cyber roles, including four years as OSD (IT and Cyber Security) to the Chief of the Army Staff, where he delivered ARMAAN, the Army’s first Aadhaar-enabled platform.
With a team from engineering, product, audit and finance
Integrations
Works with the systems you already run
Keep evidence in Netra’s cloud or your own storage, bring in the lists your teams already keep, and take reports out as PDFs.
- 8 storage providers for your Document Vault
- Imports from CSV, Excel and OpenDocument files
- One-click policy, board and audit reports
Frequently Asked Questions
Everything you need to know about Netra
See your own frameworks
running in Netra
A 25-minute demo on the frameworks that matter to you. If it helps your decision, a tightly scoped proof of concept.