Insights on compliance that gets done
Regulatory updates, framework guidance and practical notes on audits, evidence and third-party risk, from the Netra team.
Latest
A vCISO onboarding checklist for the first 90 days with a new client
A practical sequence for a vCISO or MSSP taking on a new client: what to establish in the first 30, 60 and 90 days, and what evidence to leave behind.
24 October 2026 6 min read
Read article
A Board and IT Strategy Committee reporting pack for RBI’s 2026 cybersecurity Directions
What RBI’s 2026 cyber Directions expect to reach the Board, the IT Strategy Committee and the Audit Committee, by when, and a pack structure to hold the evidence.
24 October 2026 7 min read
SOC 2 report guide for Indian service providers selling to US and global customers
What a SOC 2 report is, how the Trust Services Criteria apply, Type 1 versus Type 2, the CPA firm's role and what auditors sample. Written for Indian providers.
24 October 2026 9 min read
ISO/IEC 27001:2022 certification in India: the management system, Annex A, the audit stages and what auditors ask for
What ISO/IEC 27001:2022 requires, how its 93 Annex A controls and the Statement of Applicability fit, how certification audits run, and what to have ready.
24 October 2026 8 min read
The MeitY Comprehensive Security Audit (CSA) checklist: who answers it, how the audit runs and what reviewers expect
CERT-In’s 2025 audit guidelines make a 282-point checklist the default audit scope for sensitive government systems. What we could verify, and how to prepare.
24 October 2026 8 min read
RBI’s 2026 cybersecurity Directions for All India Financial Institutions: what the Board, the CISO and auditors need to show
The 2026 Directions name five All India Financial Institutions and set out governance, baseline controls, a SOC and IS audit. Here is what they ask.
24 October 2026 8 min read
RBI’s 2026 cybersecurity Directions for Credit Information Companies: what the Board, the CISO and auditors need to show
The 2026 Directions set out governance, baseline controls, a security operations centre and IS audit for Credit Information Companies. Here is what they ask.
24 October 2026 8 min read
RBI’s 2026 cybersecurity Directions for Payments Banks: what the Board, the CISO and auditors have to show
Payments Banks now have their own cyber Directions, issued 31 July 2026. What they ask of the Board, CISO, CSOC and IS audit, and the evidence behind each duty.
24 October 2026 8 min read
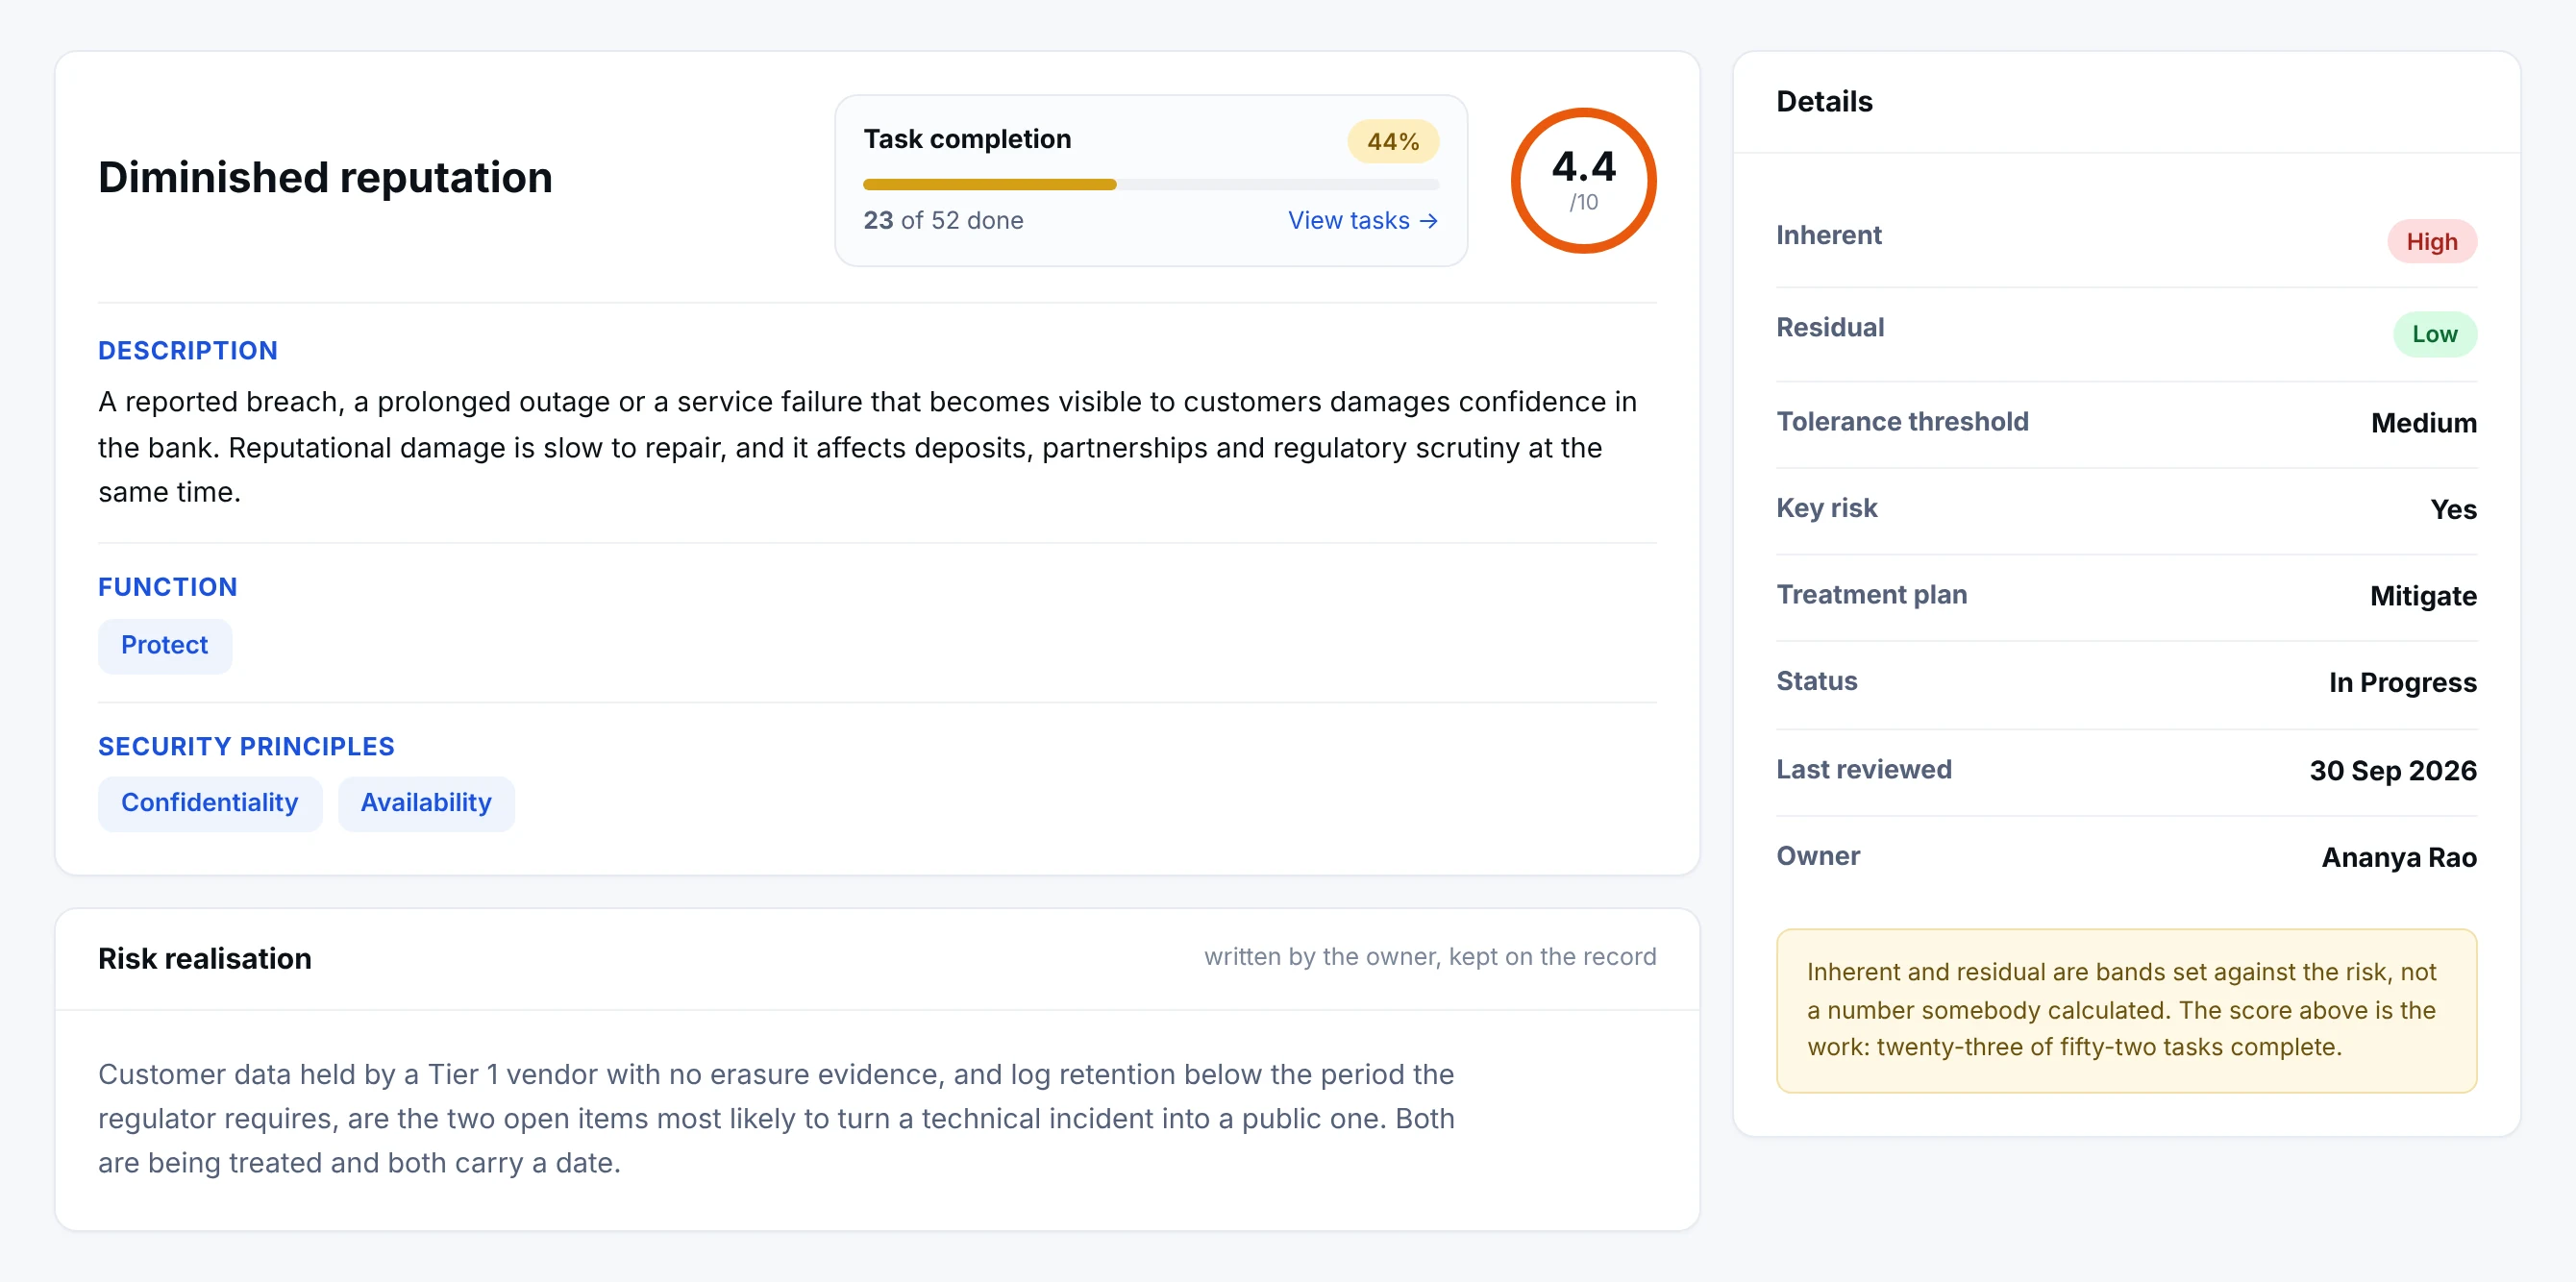
RBI’s 2026 cybersecurity Directions for Small Finance Banks: what the Board, the CISO and internal audit have to run
Small Finance Banks have their own cyber Directions, issued 31 July 2026. What they ask of the Board, CISO, CSOC and IS audit, and the evidence for each duty.
24 October 2026 8 min read
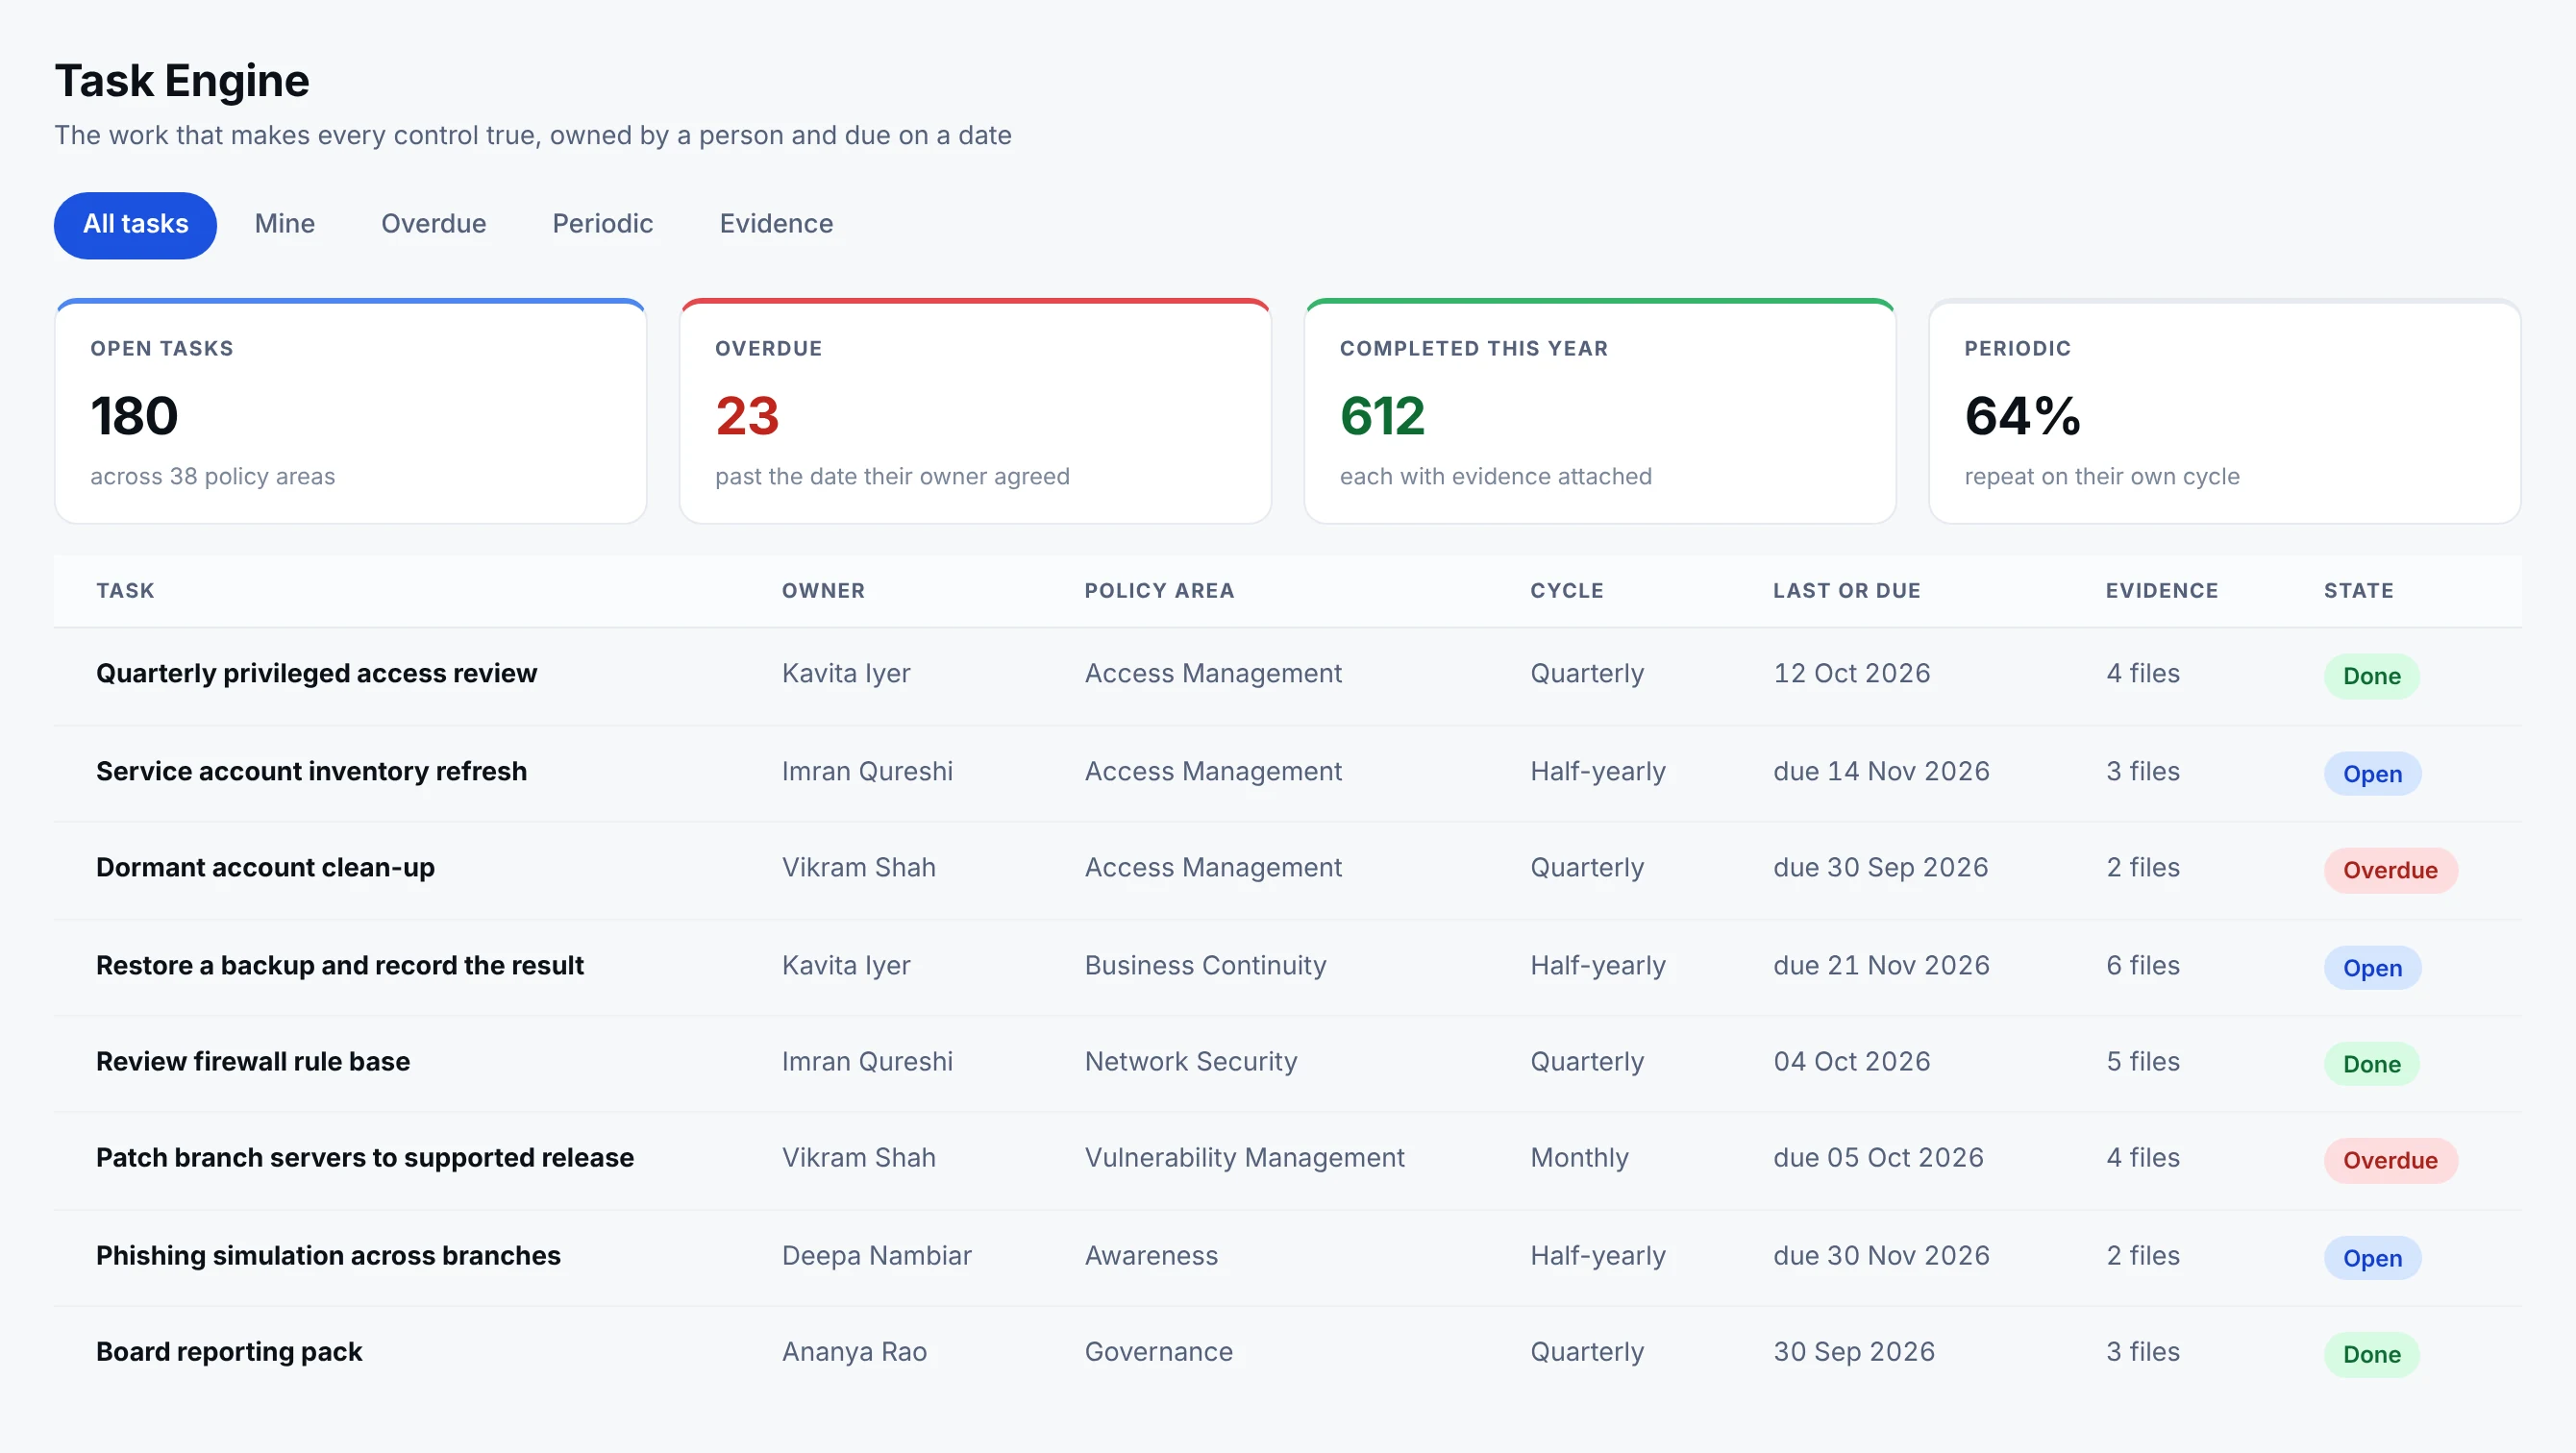
RBI’s 2026 cybersecurity Directions for NBFCs: which chapter applies to you, and what it asks
RBI’s 2026 Directions give each NBFC one of three chapters, set by layer and asset size. See how to find yours, what it asks, and what evidence to keep.
24 October 2026 8 min read
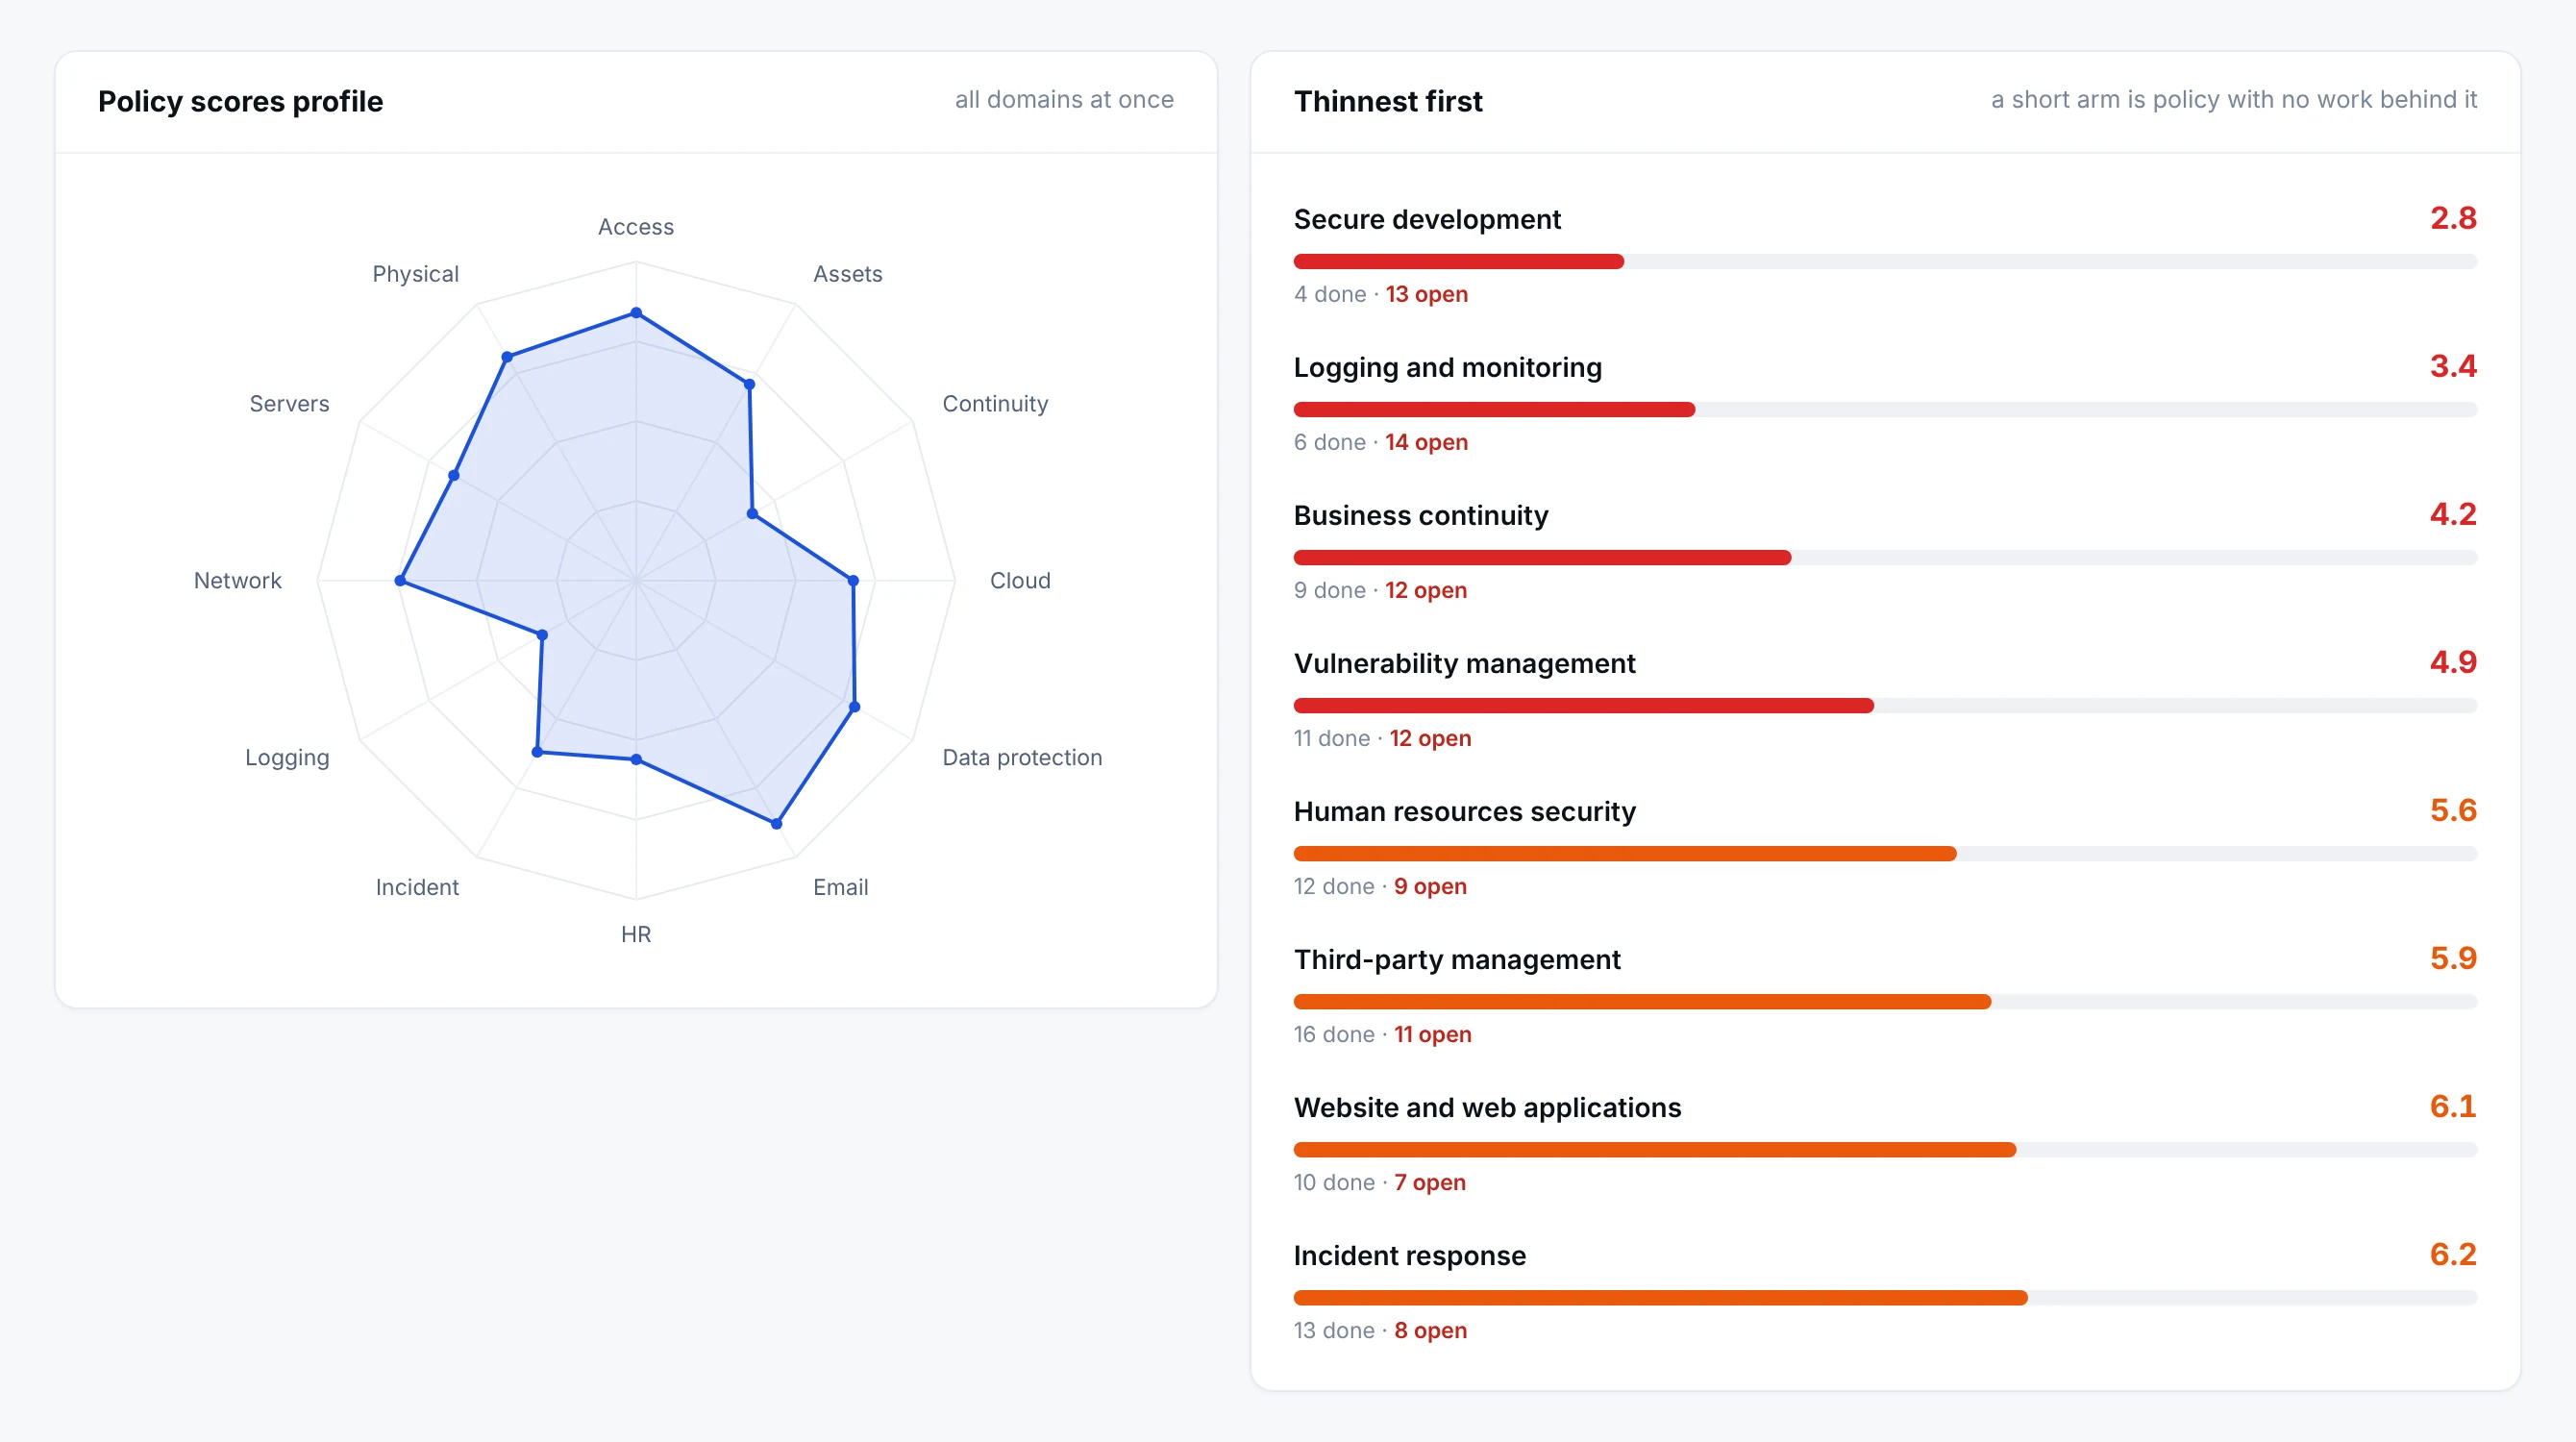
RBI’s 2026 cybersecurity Directions for urban co-operative banks: the four levels, and what each one asks
RBI’s 2026 Directions sort urban co-operative banks into four levels. See how to find your level, what each level adds, and the evidence a supervisor will want.
24 October 2026 8 min read
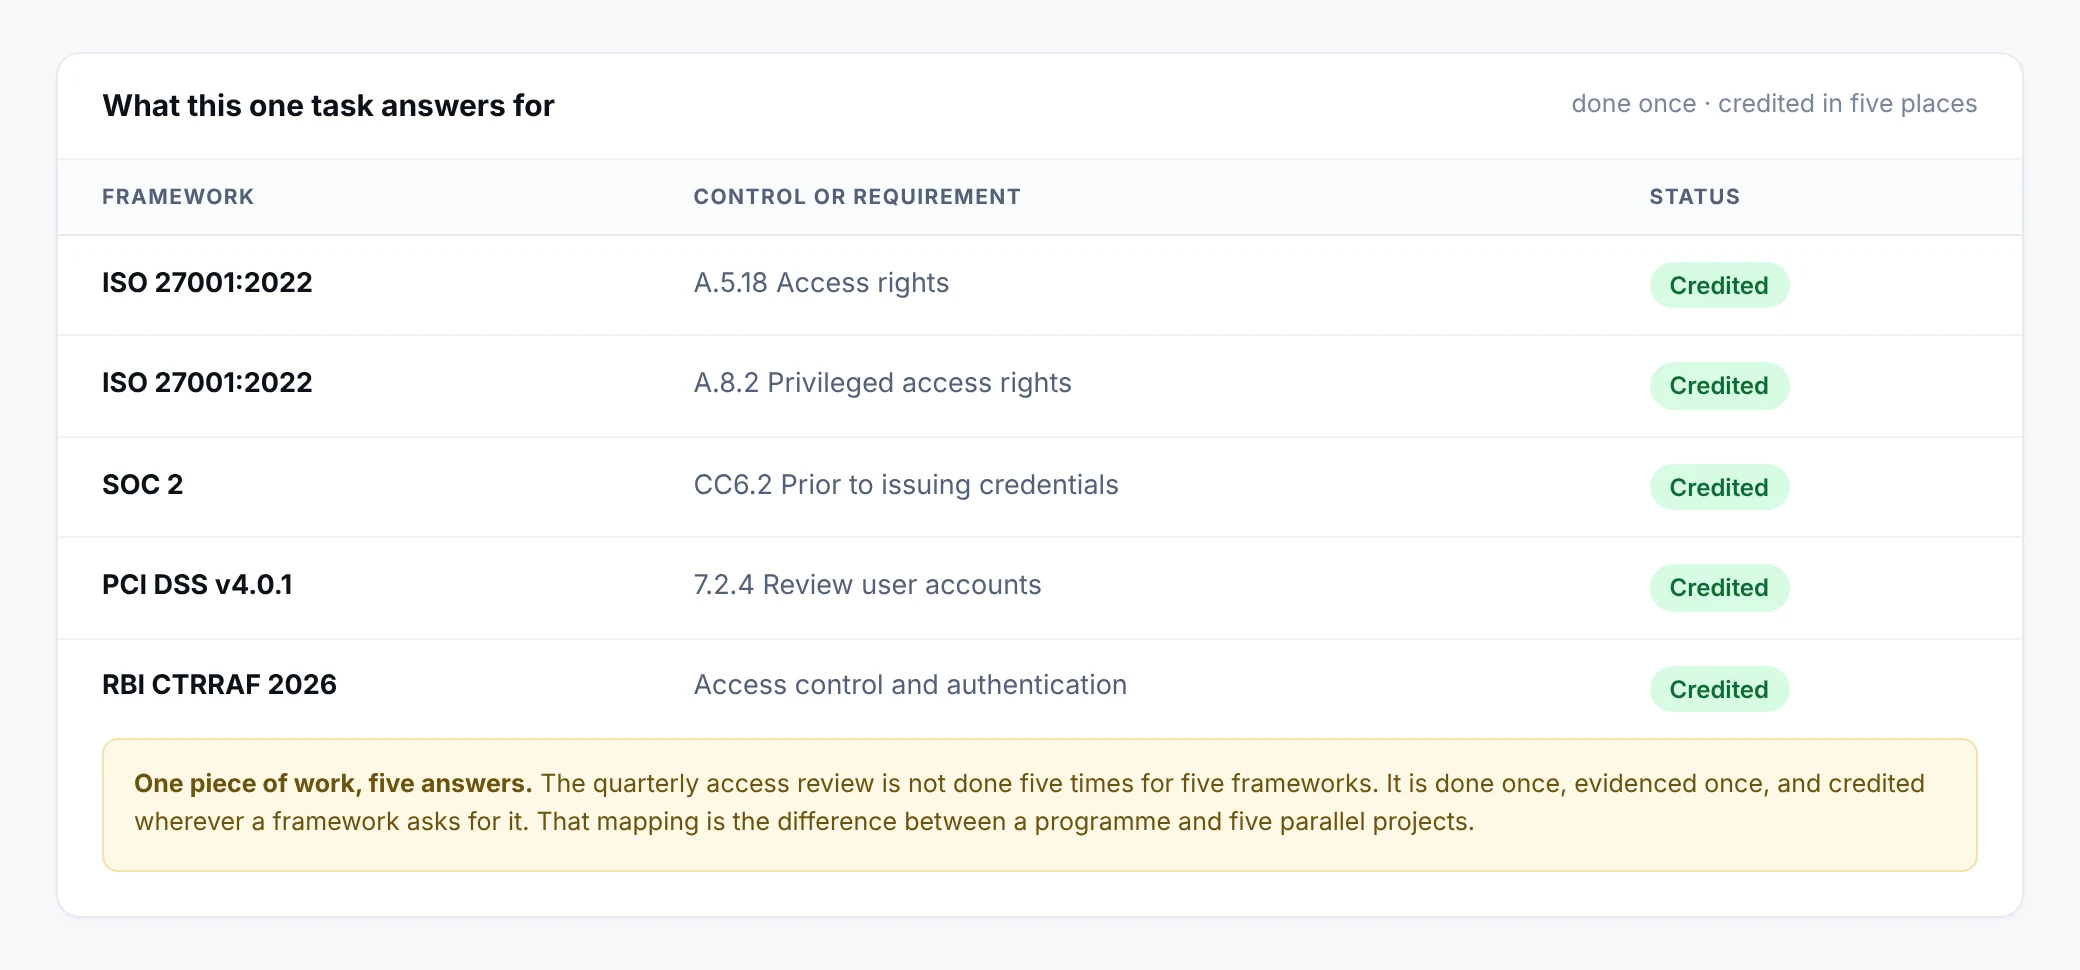
CERT-IN 6-hour incident reporting: what your organisation has to be able to show
The CERT-IN Directions ask for incident reports within six hours, logs kept in India for 180 days and synchronised clocks. Here is what that means in practice, and how to be ready before an incident.
21 October 2026 6 min read
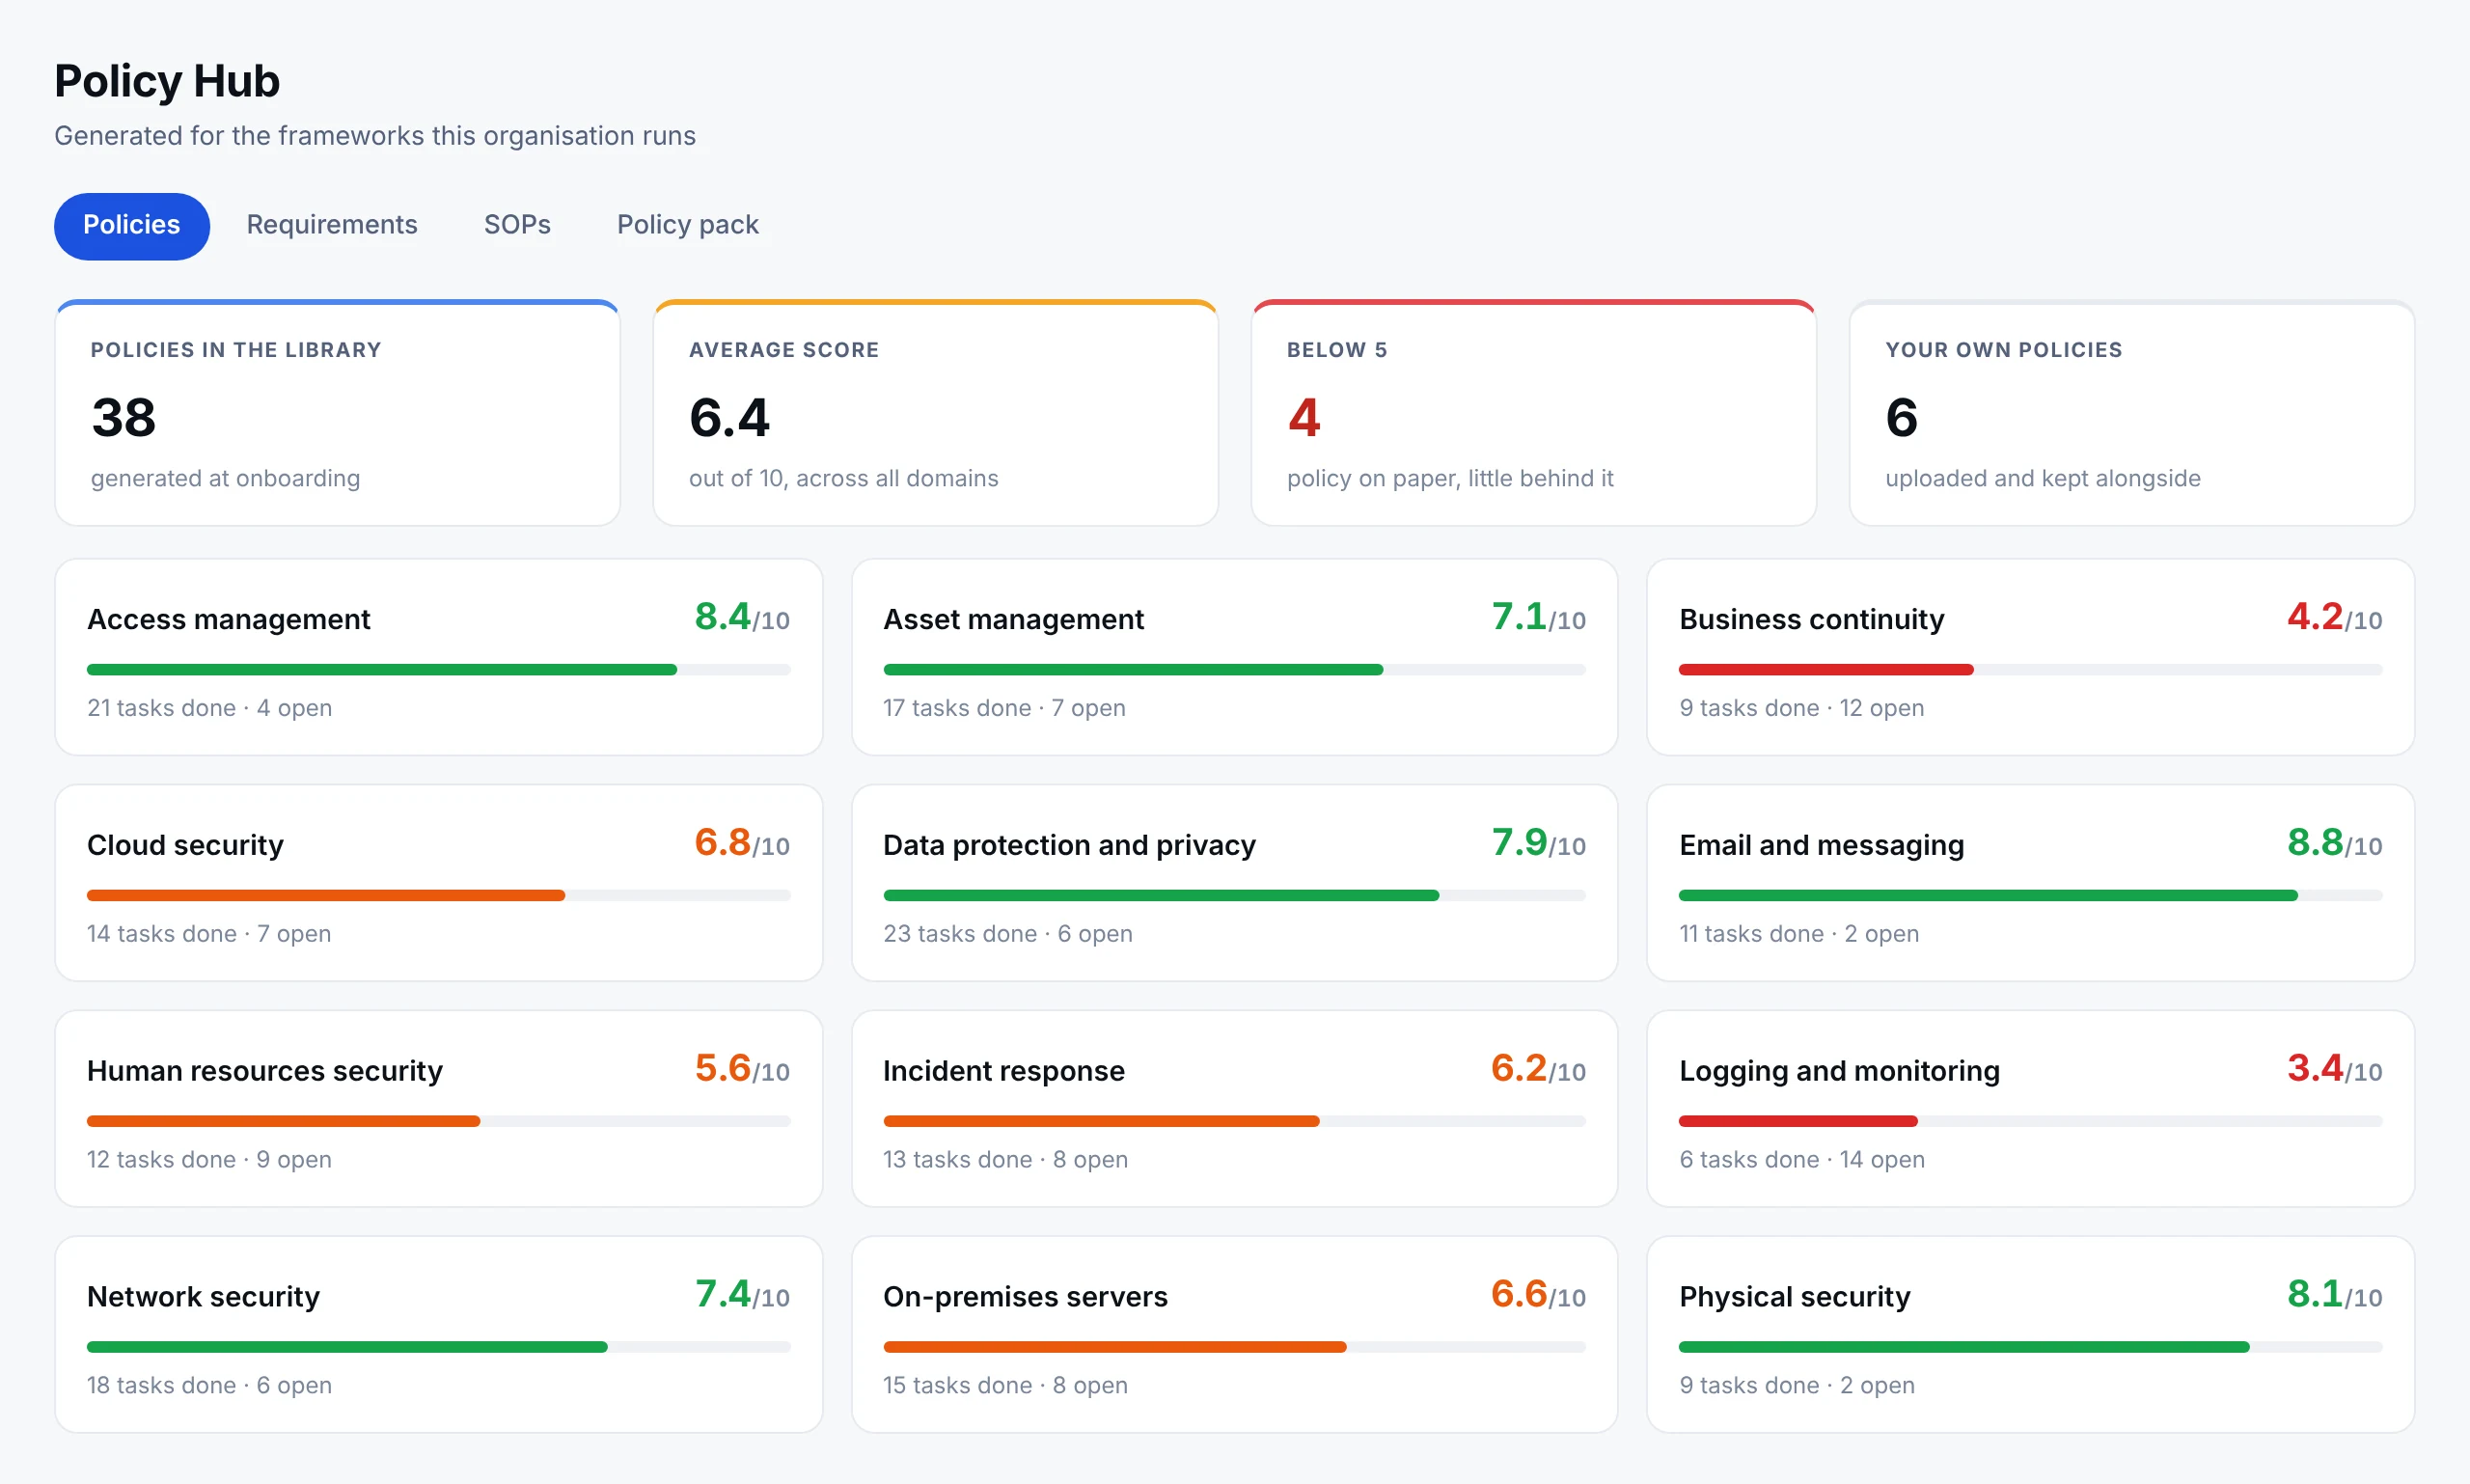
DPDP Act compliance in India: a practical checklist before May 2027
The DPDP Rules were notified on 13 November 2025 and the main duties for data fiduciaries start on 13 May 2027. Here is what the Rules ask for, and a working checklist.
14 October 2026 7 min read
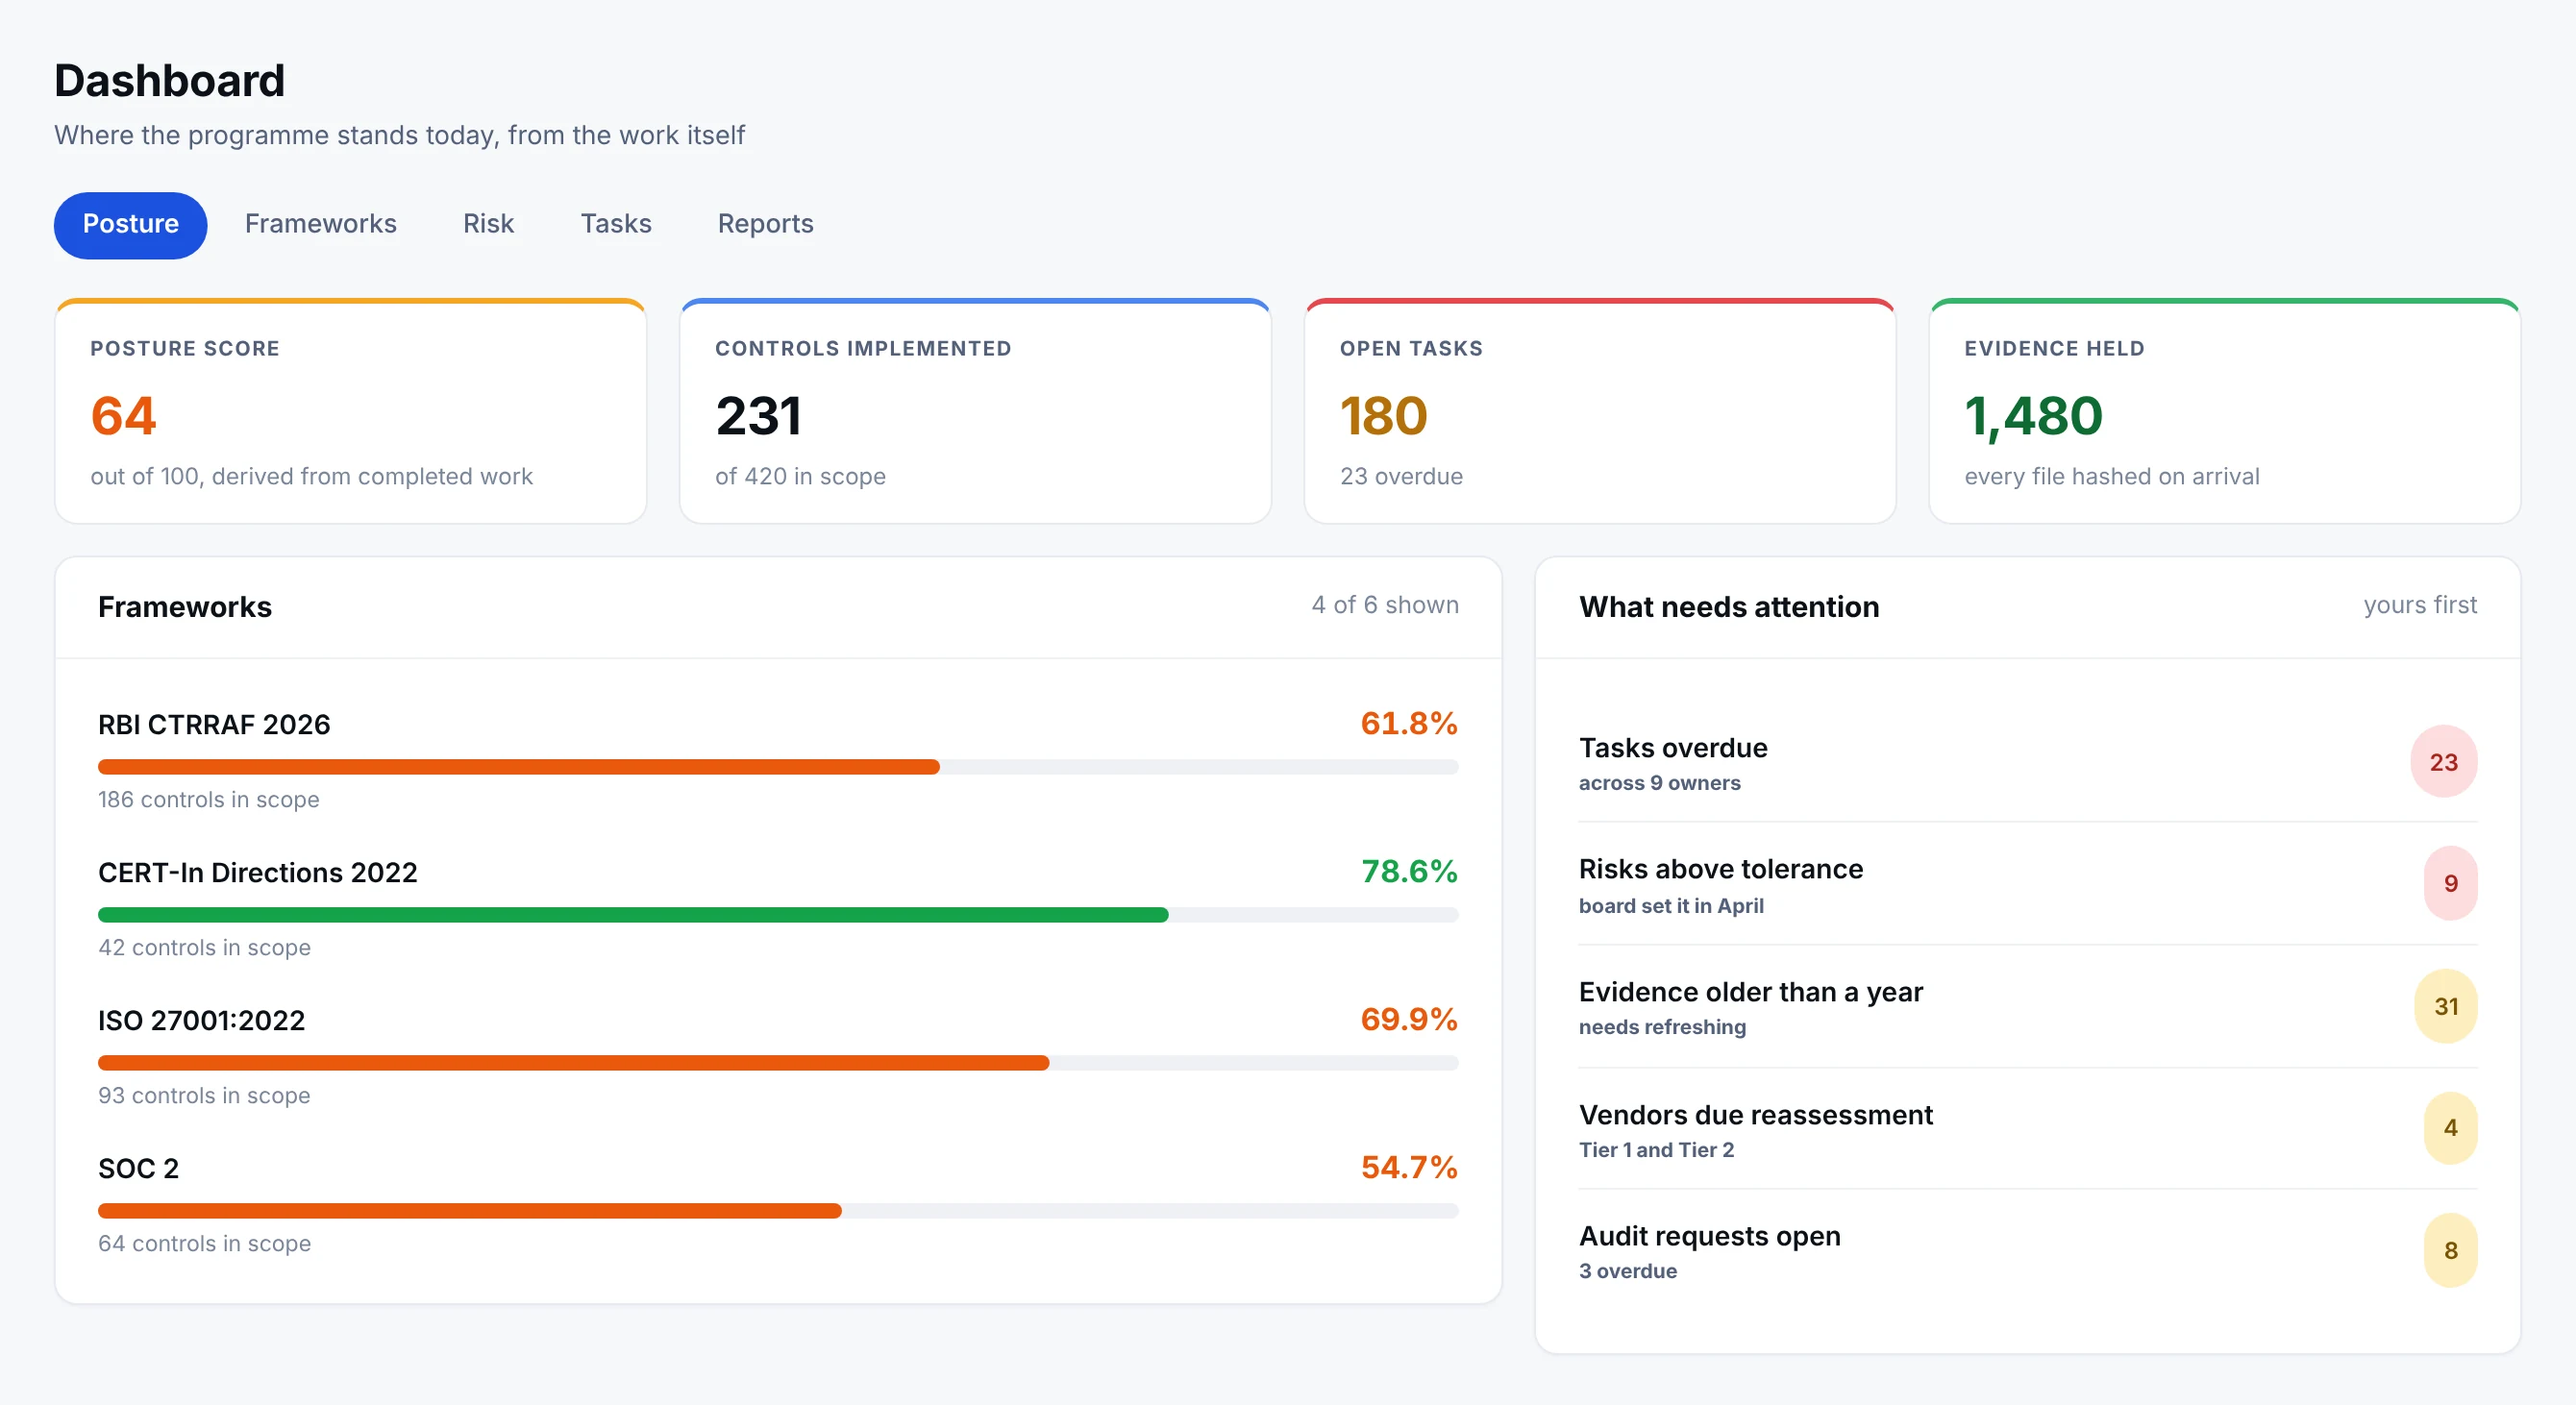
RBI’s 2026 cybersecurity Directions for commercial banks: what the Board, the CISO and auditors need to know
The new Directions bring IT governance, cyber risk, baseline controls, a security operations centre and IS audit into one text. Here is what they ask of a commercial bank, and where the work usually gets stuck.
6 October 2026 6 min read
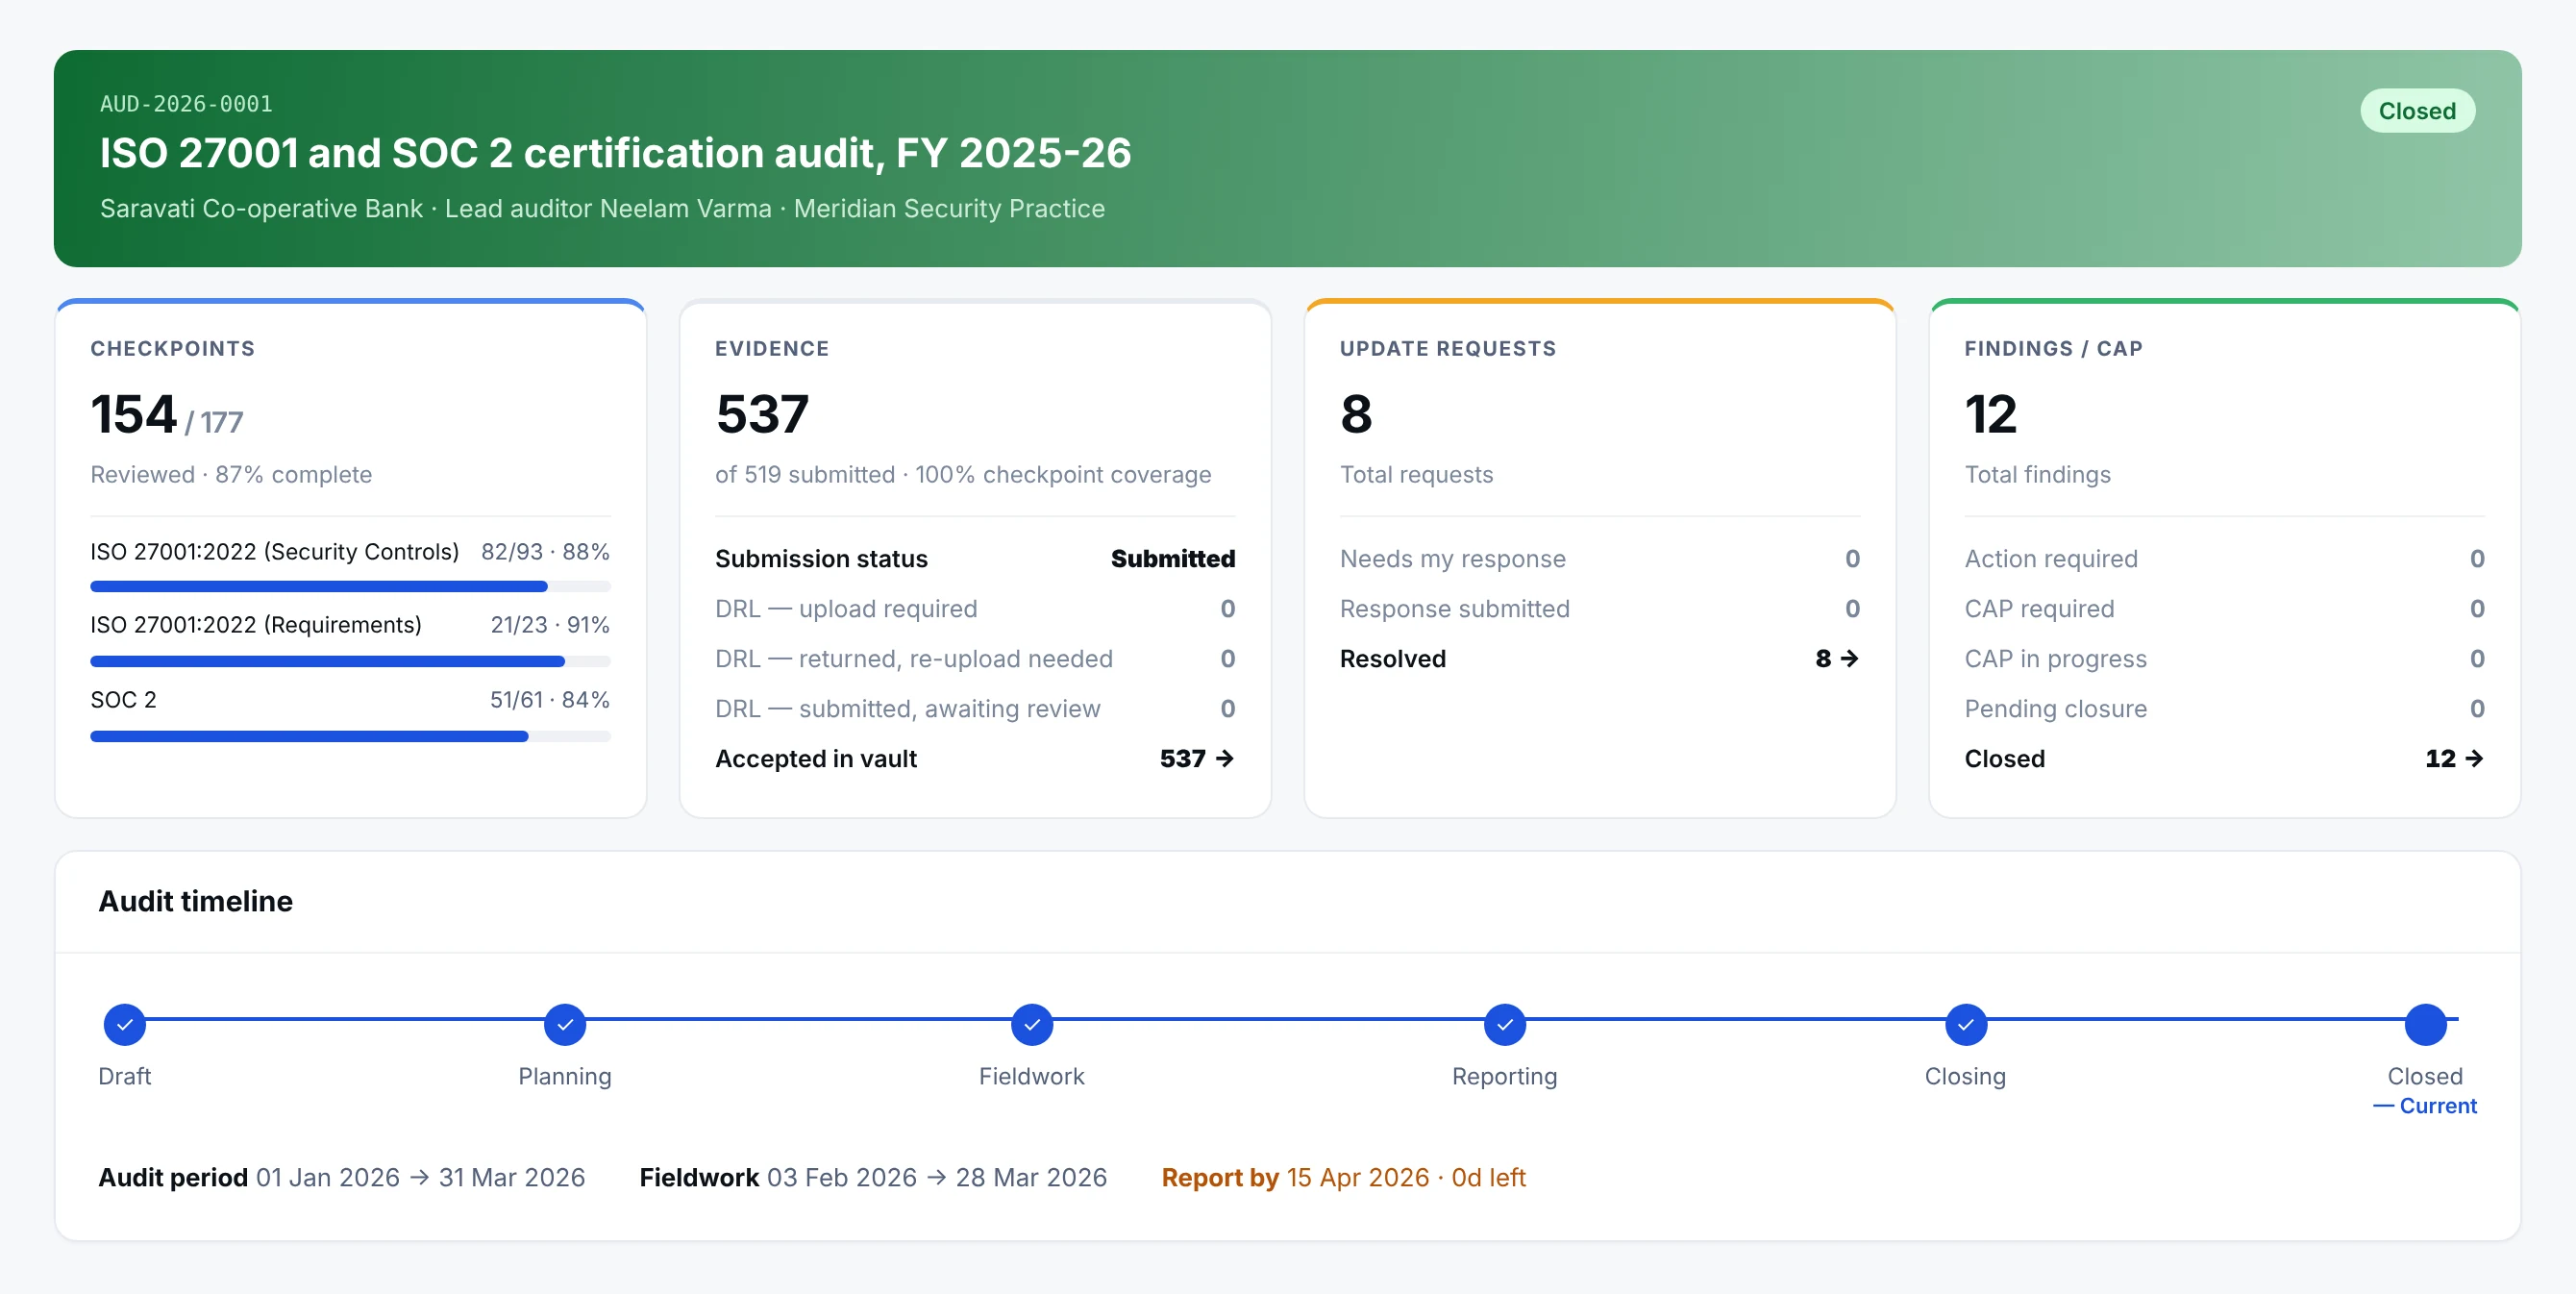
Audit readiness checklist: how to walk into an audit with evidence already in place
Most audit stress comes from collecting evidence after the audit is announced. A checklist for being ready all year, for ISO 27001, SOC 2 or a regulatory IS audit.
24 September 2026 6 min read
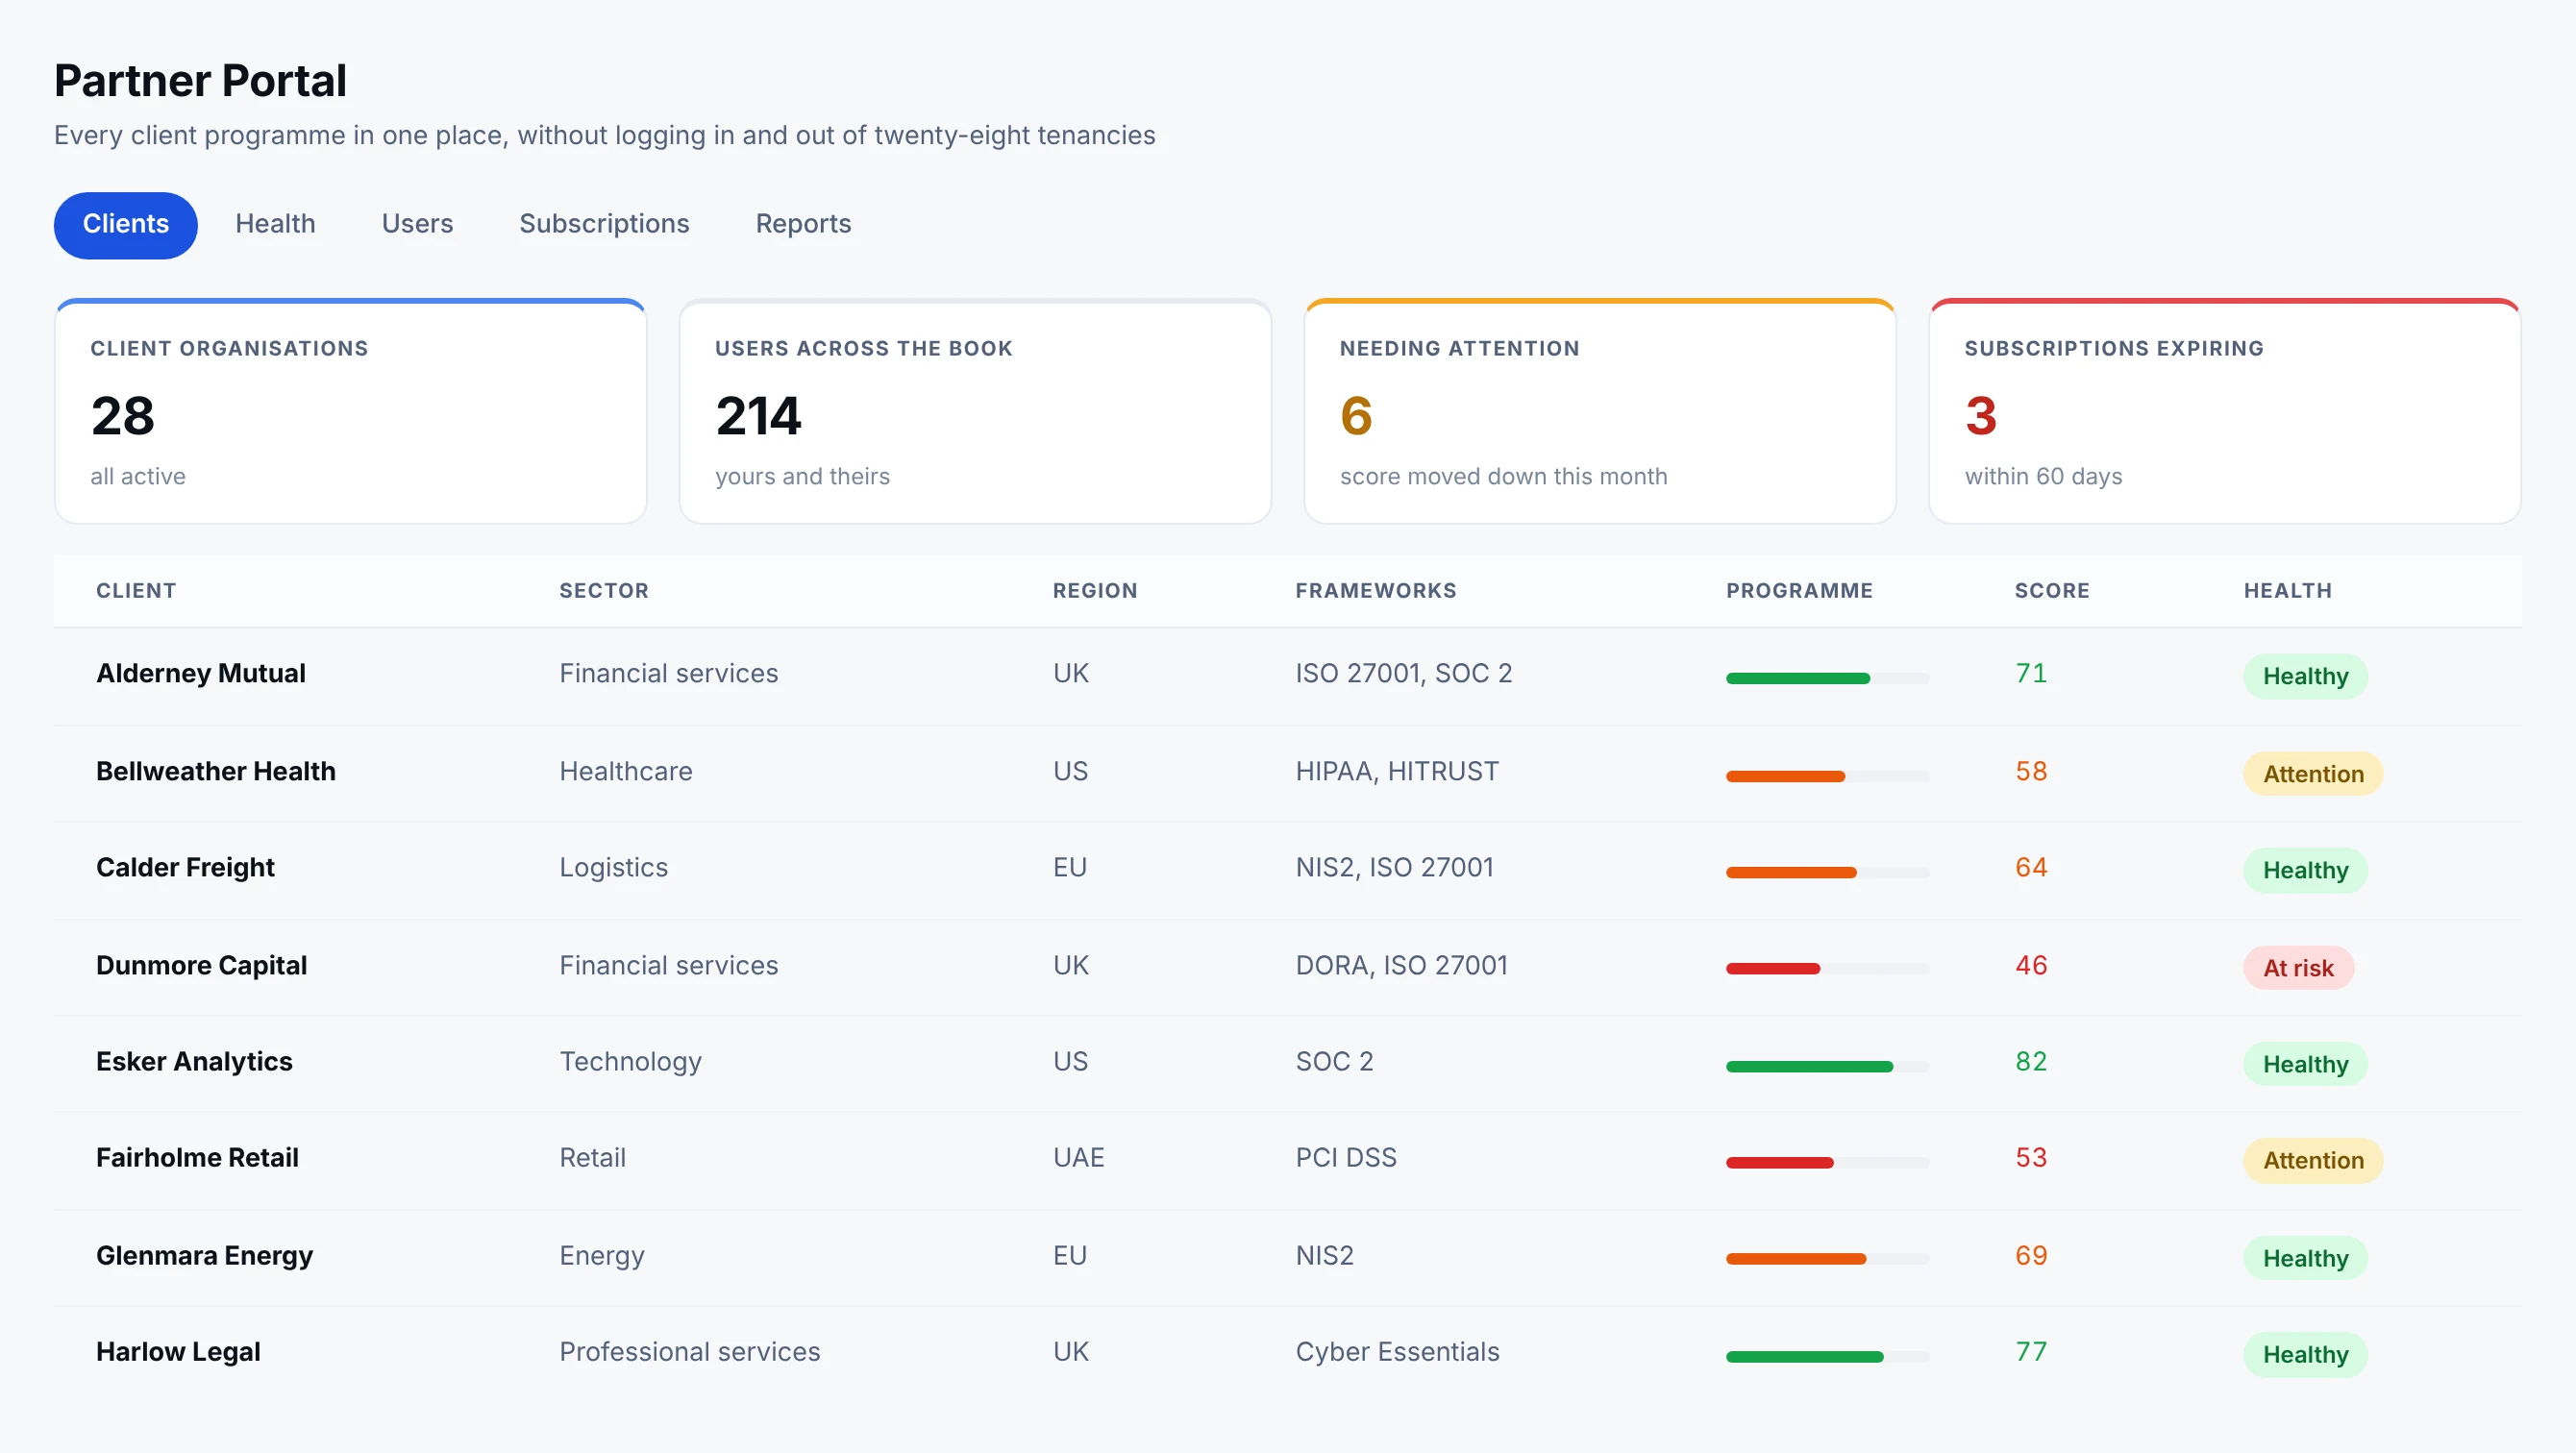
How vCISOs and MSSPs can run compliance for many clients without adding headcount
A vCISO practice grows by adding clients, and the compliance work grows with it. Here is how practices stay in control of ten or fifty clients, and where a Compliance & Audit OS fits.
10 September 2026 6 min read
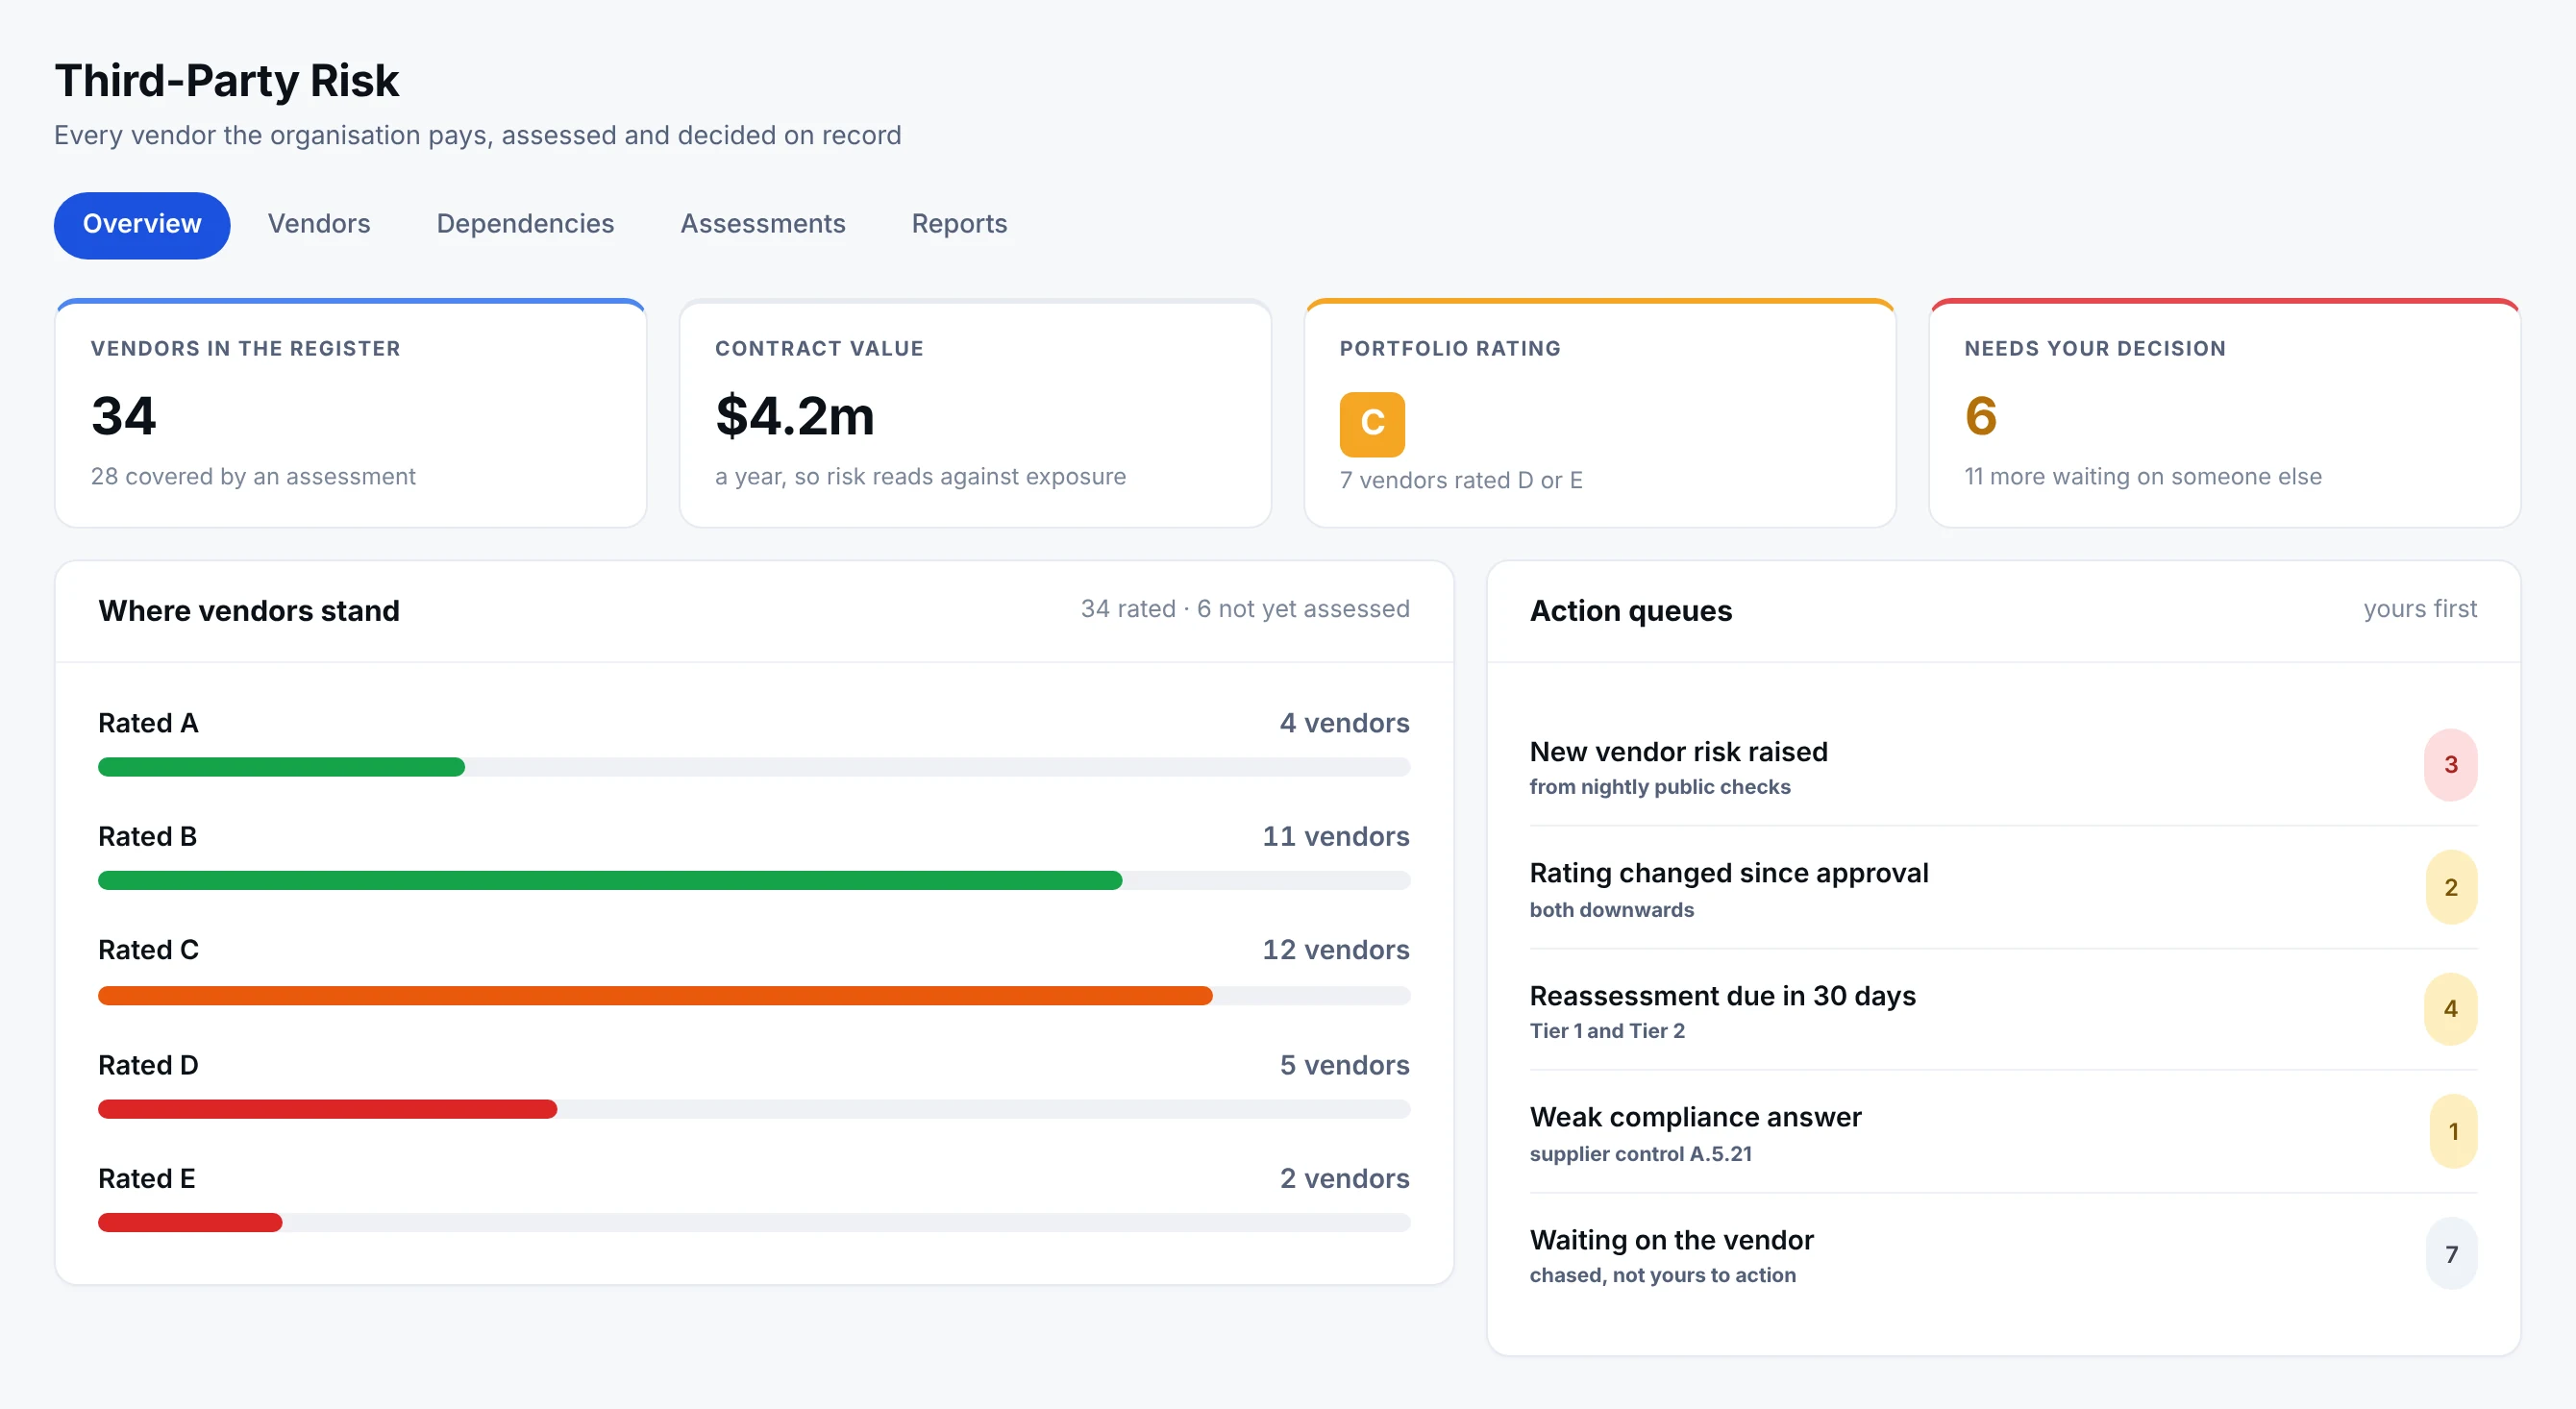
Third-party risk management: a vendor assessment checklist that survives an audit
Most organisations know their vendors. Fewer can show how each was assessed, rated and approved. A practical checklist for third-party risk management, from discovery to Board decision.
27 August 2026 6 min read
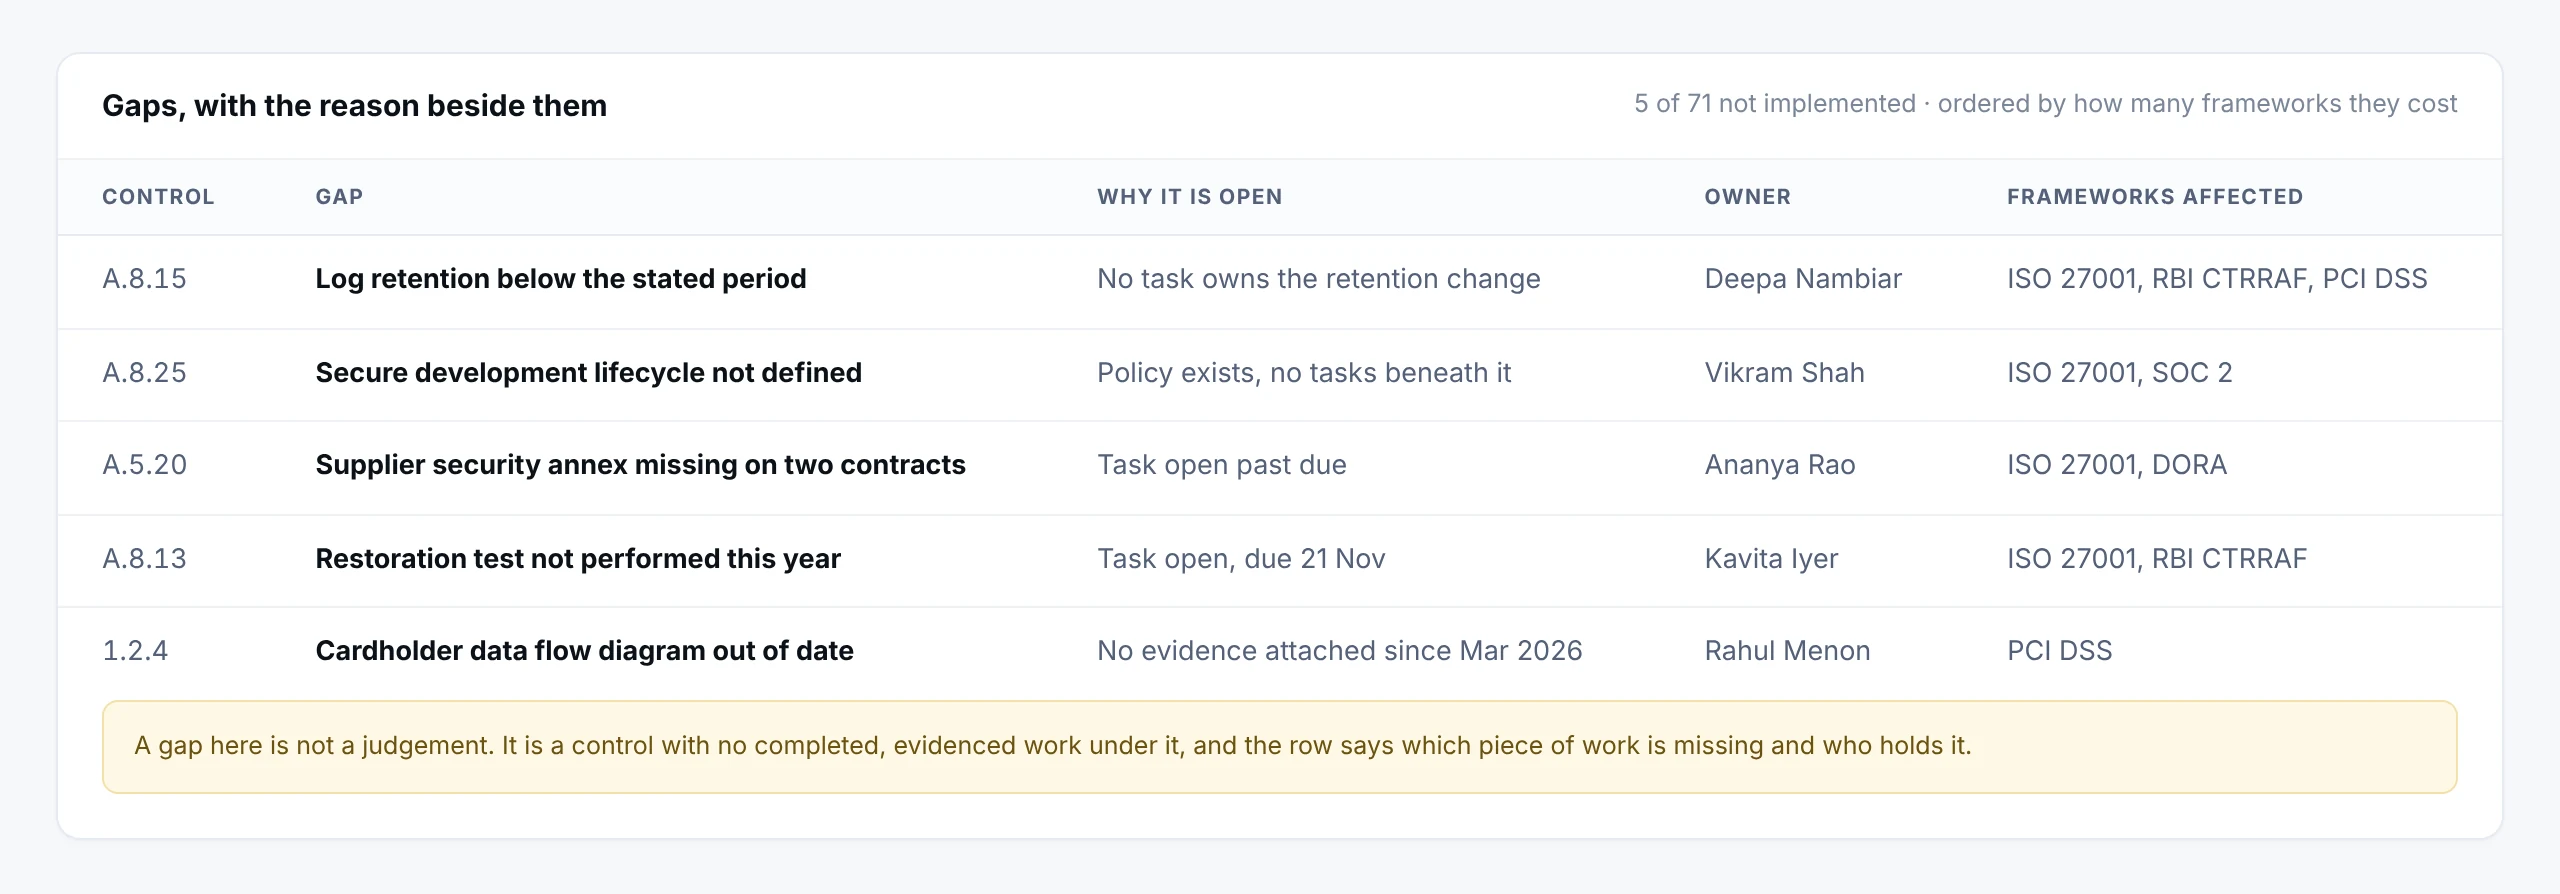
SOC 2 or ISO 27001: which one does your customer actually want?
SOC 2 is an attestation report and ISO 27001 is a certification. They answer the same question in different ways. Here is how to choose, and how to avoid doing the work twice.
13 August 2026 6 min read