Key takeaways
- SOC 2 is an attestation report by a CPA firm. ISO 27001 is a certificate from an accredited body.
- Ask your last five serious prospects which they asked for. That beats any general rule.
- The two share most of their controls, so run each control once and map it to both.
- Many service providers end up with both. Sequence them by the next big deal.
Most security questionnaires eventually ask for one of two things: a SOC 2 report or an ISO 27001 certificate. Teams often treat them as rivals. They are better seen as two ways to prove the same thing, which is that you protect your customers' data in a way an independent party has checked.
What each one is
SOC 2 is an examination of a service organisation's controls by an independent CPA firm, against the AICPA Trust Services Criteria. It ends in a report, not a certificate. Security is always in scope. You choose whether to add Availability, Processing Integrity, Confidentiality and Privacy, depending on what you promise customers. A Type 1 report gives an opinion on whether controls are suitably designed at a point in time. A Type 2 report also tests whether they operated effectively over a period, commonly between three and twelve months.
ISO/IEC 27001 is the international standard for an information security management system. An accredited certification body audits you against it and issues a certificate. The 2022 edition has management system requirements in Clauses 4 to 10 and 93 reference controls in Annex A, in four themes. You record which controls apply, and why, in a Statement of Applicability. Certificates to the 2013 edition could not continue after 31 October 2025.
Side by side
| Row | SOC 2 | ISO 27001 |
|---|---|---|
| What you get | A detailed report your customer reads | A certificate anyone can see |
| Who issues it | An independent CPA firm | An accredited certification body |
| Scope | The system and criteria you choose | A management system you define from your own risk assessment |
| Time | Type 1 at a point in time, Type 2 over a period | Certificate runs three years, with surveillance audits in between |
| Where buyers ask | Often US enterprise buyers | Often India, Europe, the Middle East and the public sector |
Banks and other regulated entities may ask for either, plus their own questionnaire.
How to choose
- 1Ask your last five serious prospects what they asked for. That is better evidence than any general rule.
- 2Look at where you are selling next. If the pipeline is outside India, SOC 2 may come up earlier.
- 3Decide whether you need the management system. ISO 27001 makes you run risk assessment, internal audit and management review as a routine. Some organisations want that discipline. Others only need the report.
- 4Plan for both if the market requires it. Many service providers end up with both.
Where do most of your buyers sit?
What do they ask for?
Do you want a security management system running year-round?
Answer the three questions to see a suggestion.
Indicative only. Your customers' contracts and your auditor decide what is sufficient.
Avoiding the double work
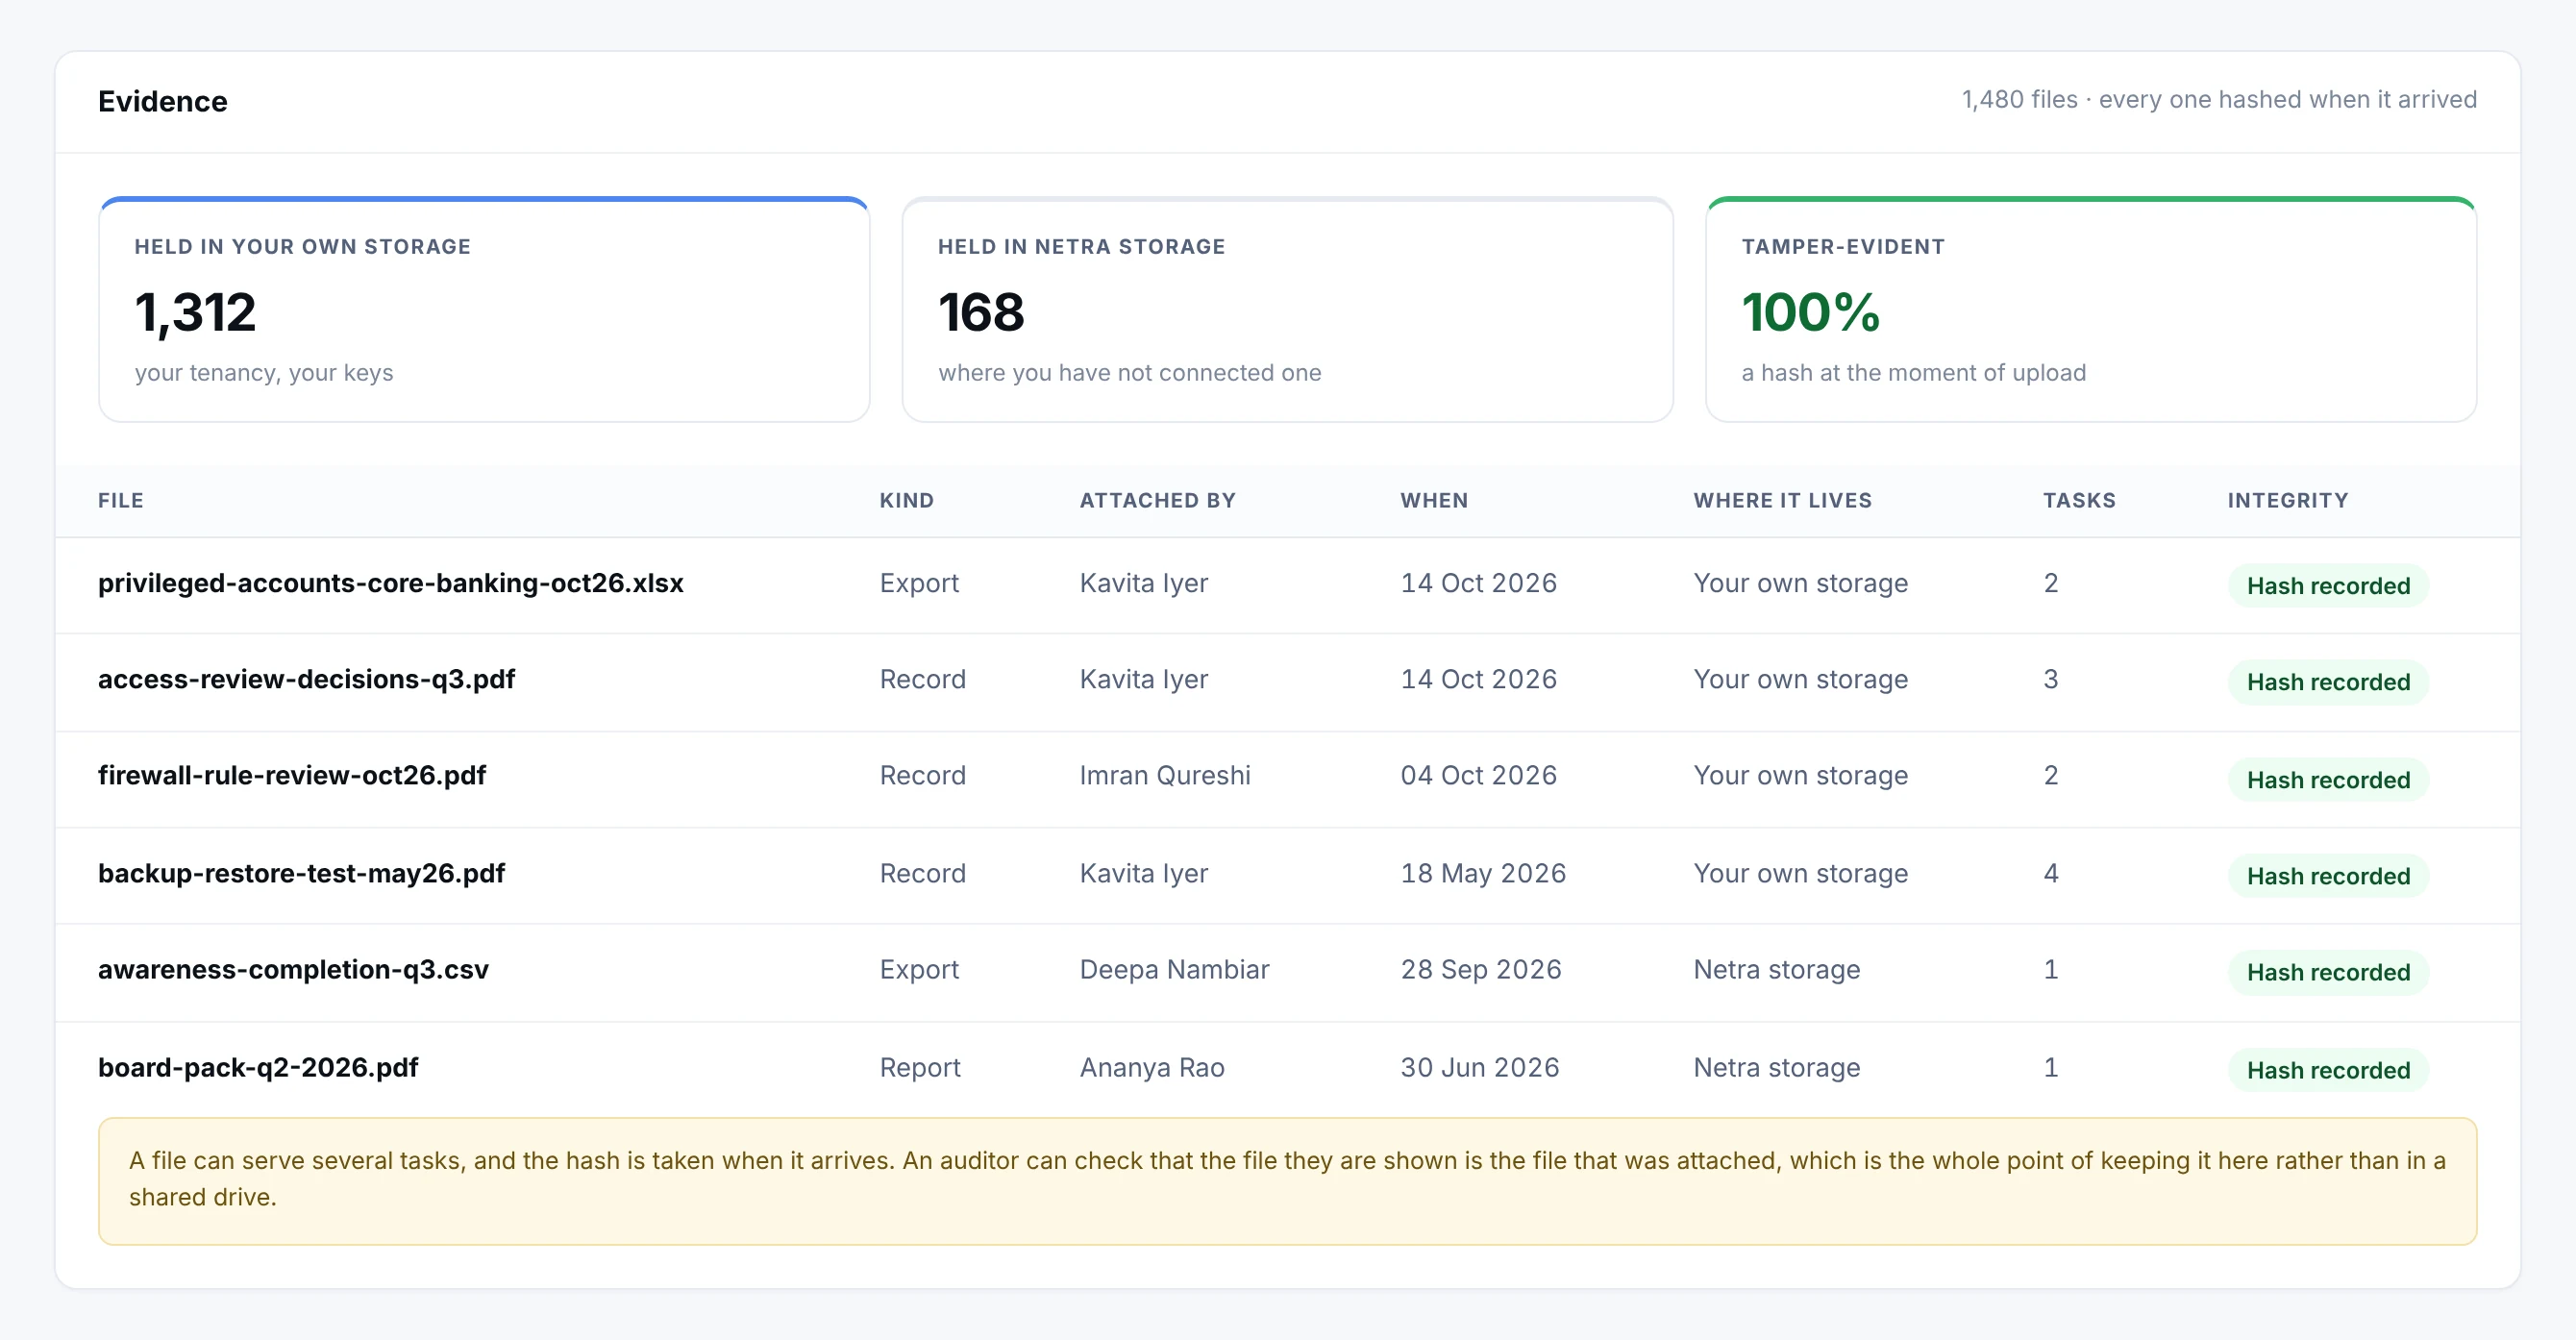
The two share a great deal. Access control, change management, vendor oversight, incident response, logging and risk assessment appear in both, worded differently. The waste comes from treating each as a separate project, with separate spreadsheets and separate evidence folders.
Tip. Run each control once, attach the evidence once, and map it to every framework it satisfies.
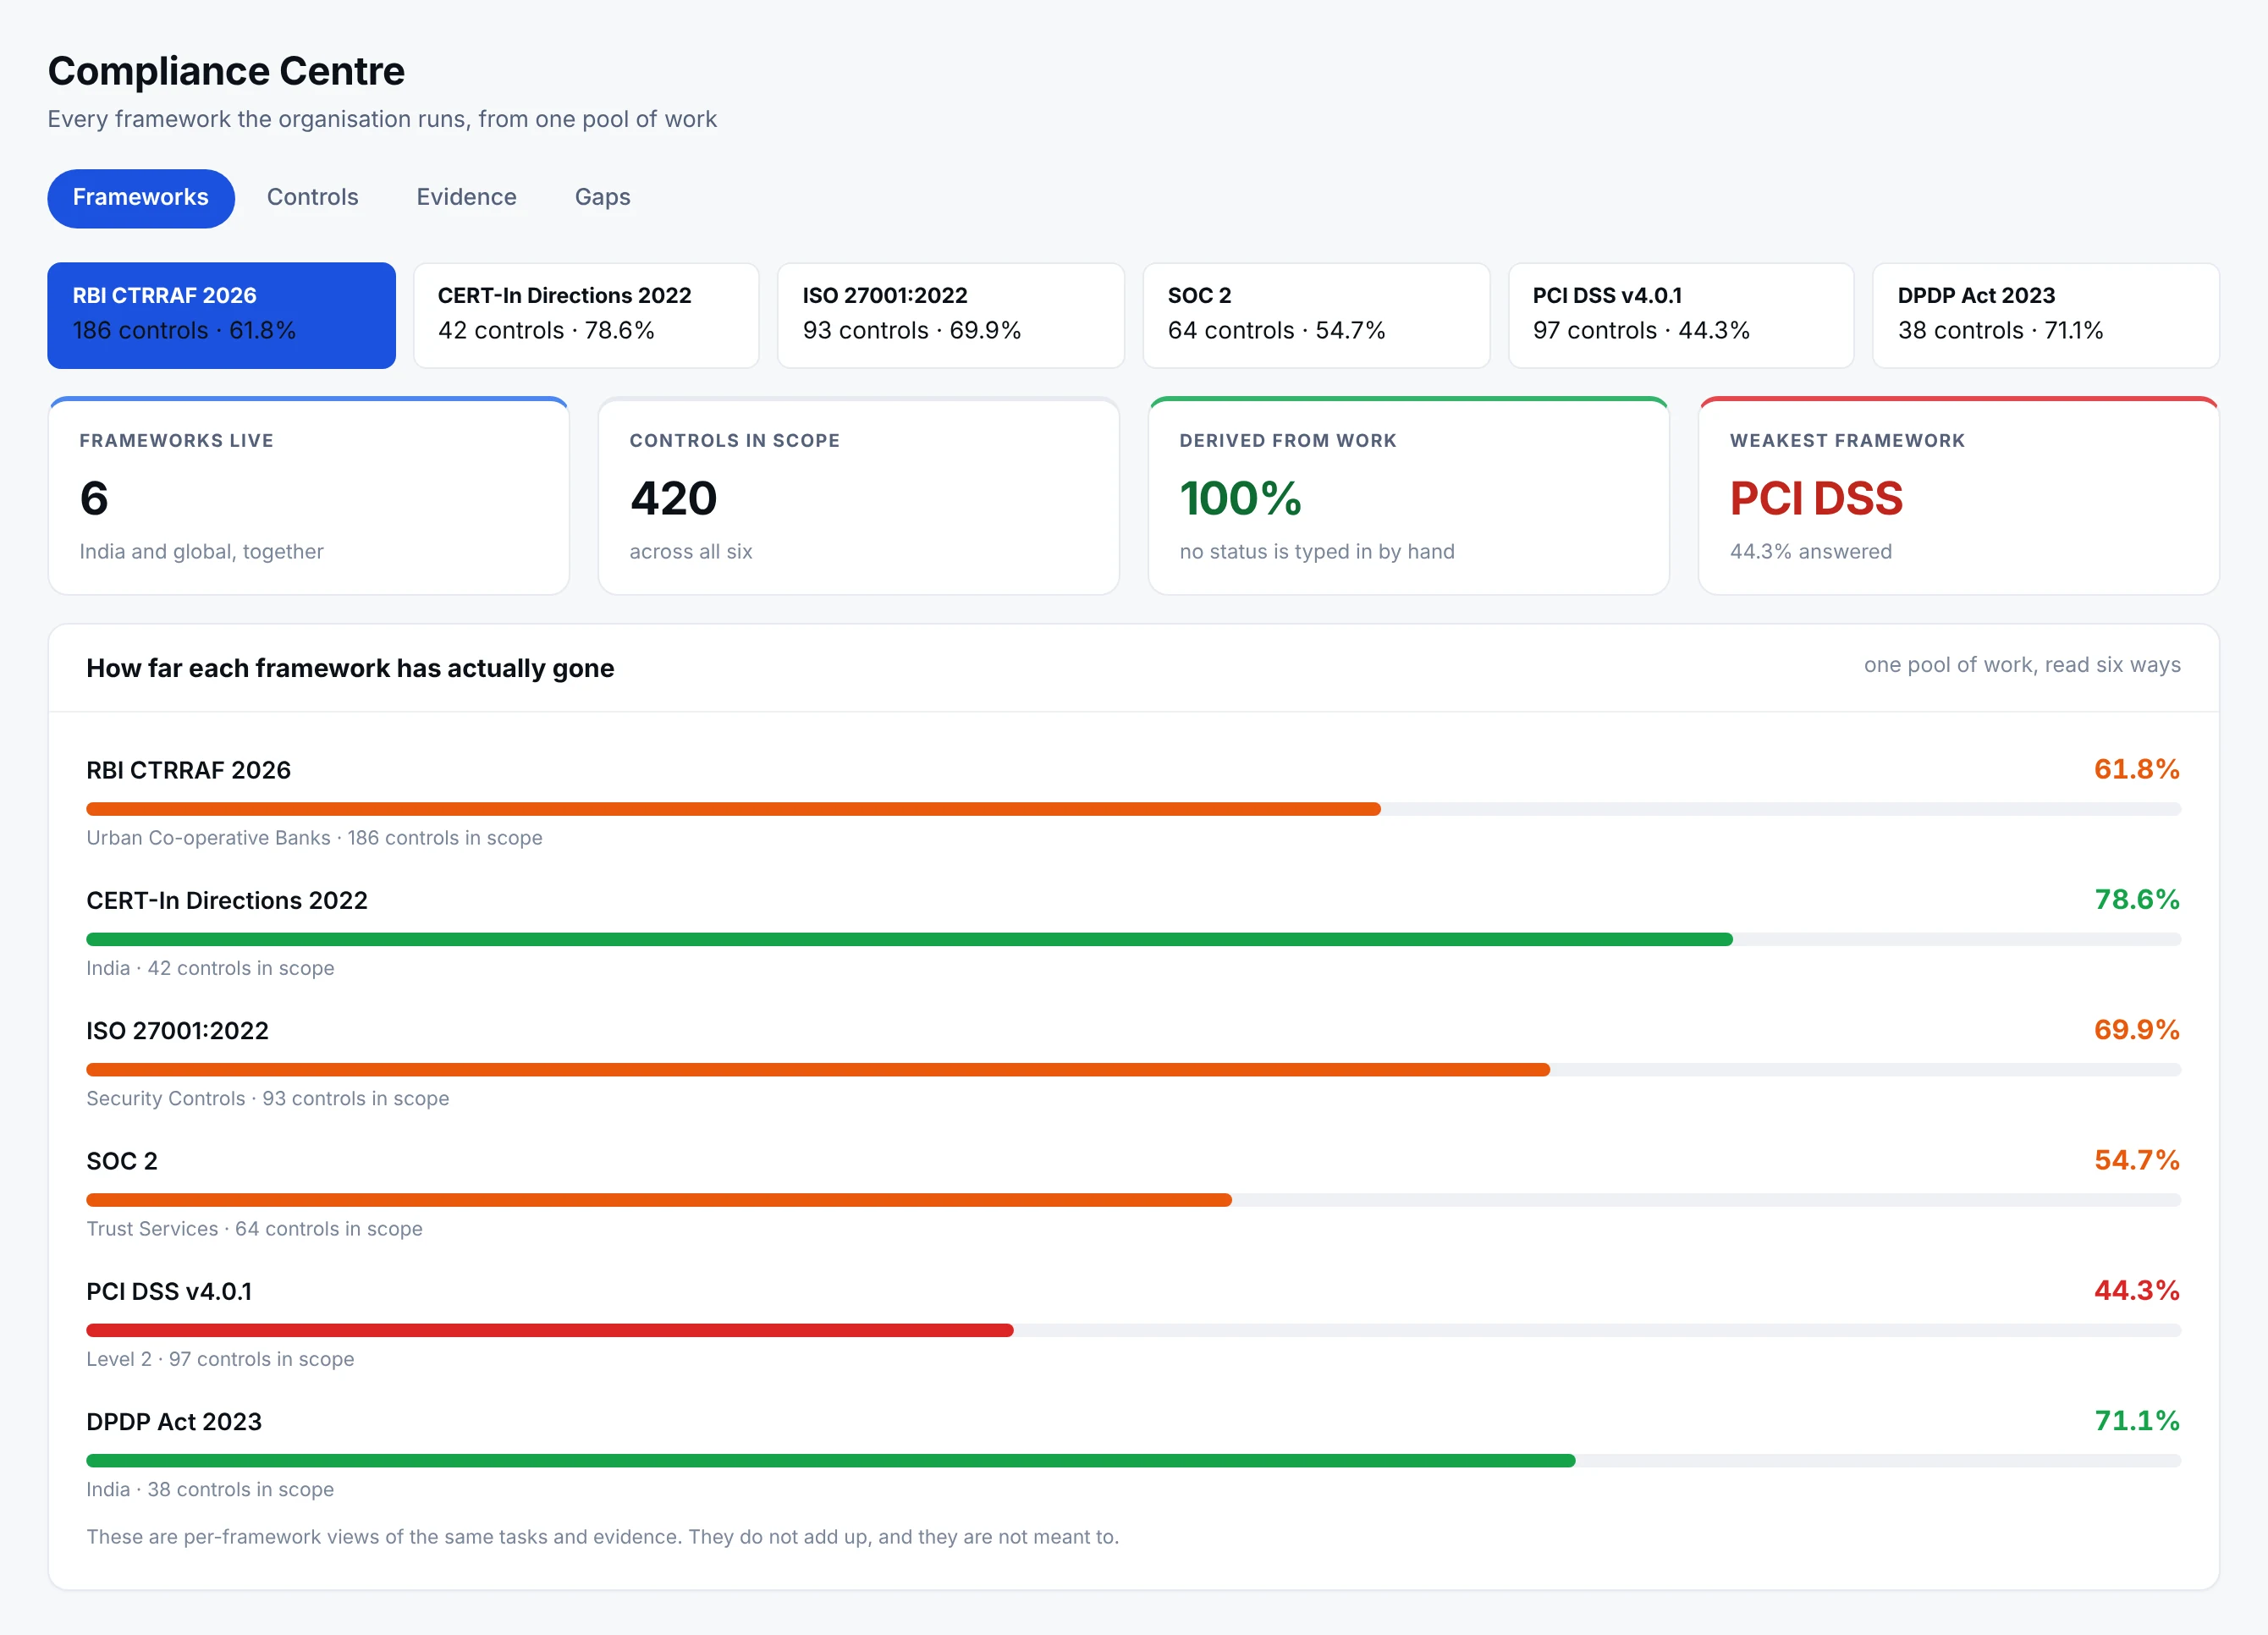
That is the idea behind Netra: one completed task can update several frameworks, policies, risks and audits. You can see how each is laid out on the SOC 2 and ISO 27001:2022 Requirements pages.
Before you start: a short checklist
This article is for general information. Your auditor or certification body decides what counts as sufficient for your scope.
Frequently asked questions
What is the difference between SOC 2 and ISO 27001?
SOC 2 is an attestation report issued by a CPA firm. ISO 27001 is a certificate issued by an accredited body.
Which one will my customers ask for?
Ask your last five serious prospects which they asked for. That is better evidence than any general rule.
Do I need both?
They share most of their controls, so each control can be run once and mapped to both. Many service providers end up with both and sequence them by the next big deal.
Run it once, satisfy both
See how one completed task can update SOC 2 and ISO 27001 together.
See it in Netra
A demo on the frameworks that matter to you.